Private endpoints
Connect your services to AWS PrivateLink endpoints to eliminate public internet exposure
With Tiger Cloud, you can connect your services to AWS PrivateLink endpoints. A private endpoint in your VPC routes traffic to your service over the AWS backbone, without crossing the public internet or requiring VPC peering. This page describes how to create a private endpoint on the AWS side, claim it in Tiger Console, attach a service to it, and publish the service hostname in your own private DNS zone.
Private networking does not turn off console passwordless connections. If your security policy requires users to connect through your private network, also turn off passwordless database access for each service.
You control DNS resolution for your service over PrivateLink. In a private hosted zone attached to your VPC, you point the standard service hostname at your VPC endpoint. Because you publish the same hostname that the public internet path uses, your connection strings and the service certificate work as before.
Prerequisites for this procedure
To follow these steps, you'll need:
- An AWS account with a VPC and a subnet for the resources you will connect to Tiger Cloud.
- Identity and Access Management (IAM) permissions configured to create VPC endpoints.
Limits
Section titled “Limits”| Limit | Value |
|---|---|
| Services per VPC endpoint | 1 |
| VPC endpoints per service | 2 |
Each VPC endpoint serves a single service, so create one endpoint for every service you connect to. Each service accepts up to two endpoints, which lets you reach it from two VPCs.
AWS also applies its own default quota of 50 interface and Gateway Load Balancer endpoints per VPC, which you can raise through AWS Support.
Availability zones
Section titled “Availability zones”Tiger Cloud serves PrivateLink from two Availability Zones in each region. Create your VPC endpoint in both of them: one for the connection to work, the second so it survives the loss of an Availability Zone.
| Region | Availability Zone IDs |
|---|---|
ap-northeast-1 | apne1-az1, apne1-az4 |
ap-south-1 | aps1-az1, aps1-az3 |
ap-southeast-1 | apse1-az1, apse1-az2 |
ap-southeast-2 | apse2-az1, apse2-az2 |
ca-central-1 | cac1-az1, cac1-az2 |
eu-central-1 | euc1-az1, euc1-az2 |
eu-central-2 | euc2-az1, euc2-az2 |
eu-west-1 | euw1-az2, euw1-az3 |
eu-west-2 | euw2-az2, euw2-az3 |
sa-east-1 | sae1-az1, sae1-az2 |
us-east-1 | use1-az1, use1-az6 |
us-east-2 | use2-az1, use2-az2 |
us-west-2 | usw2-az3, usw2-az4 |
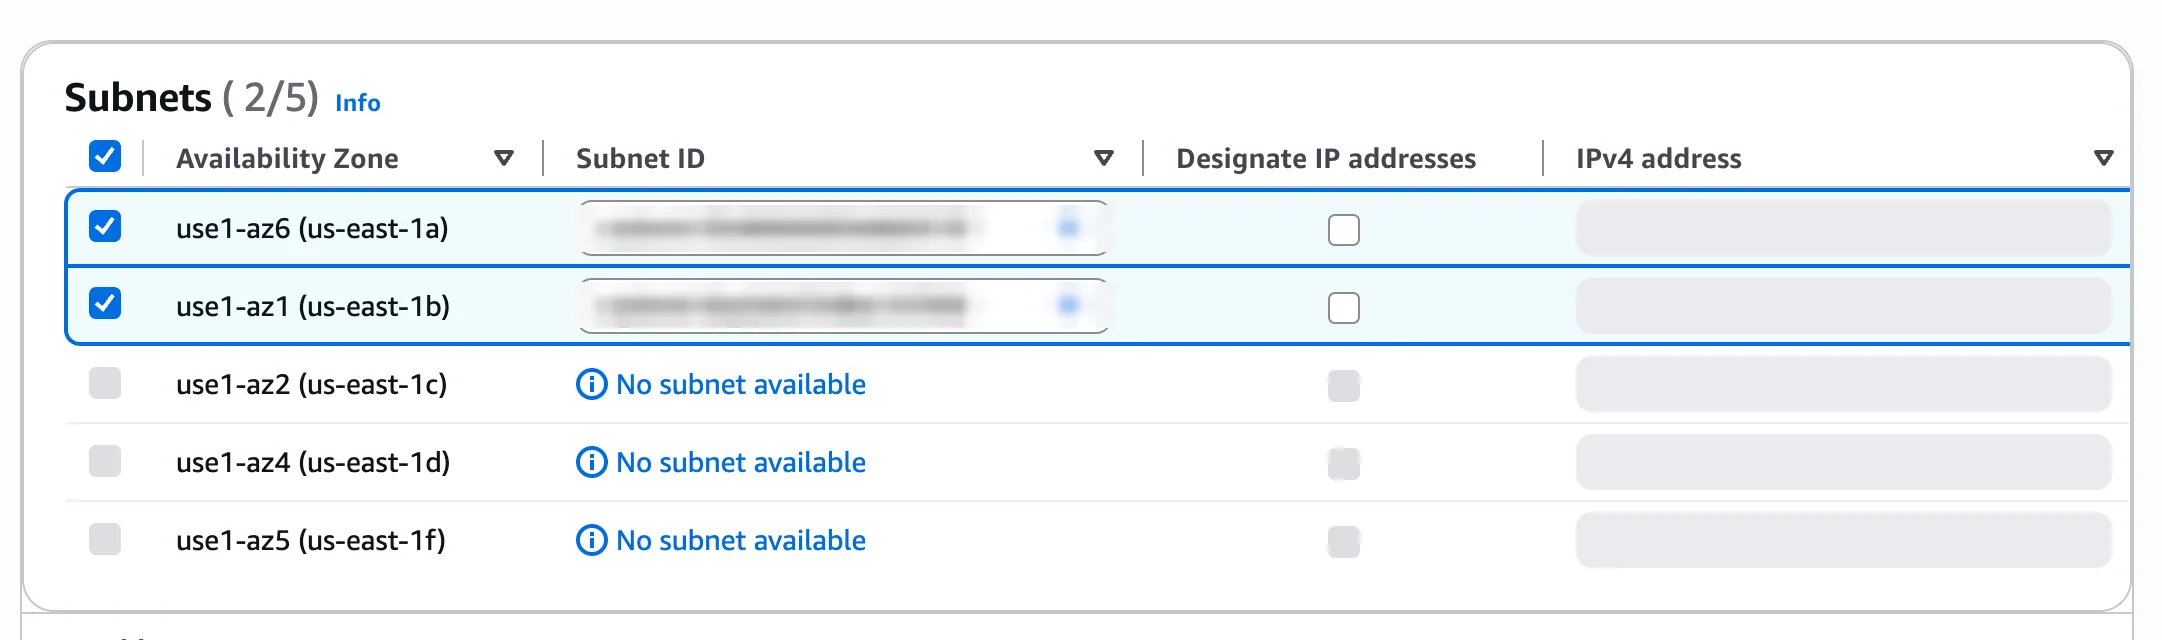
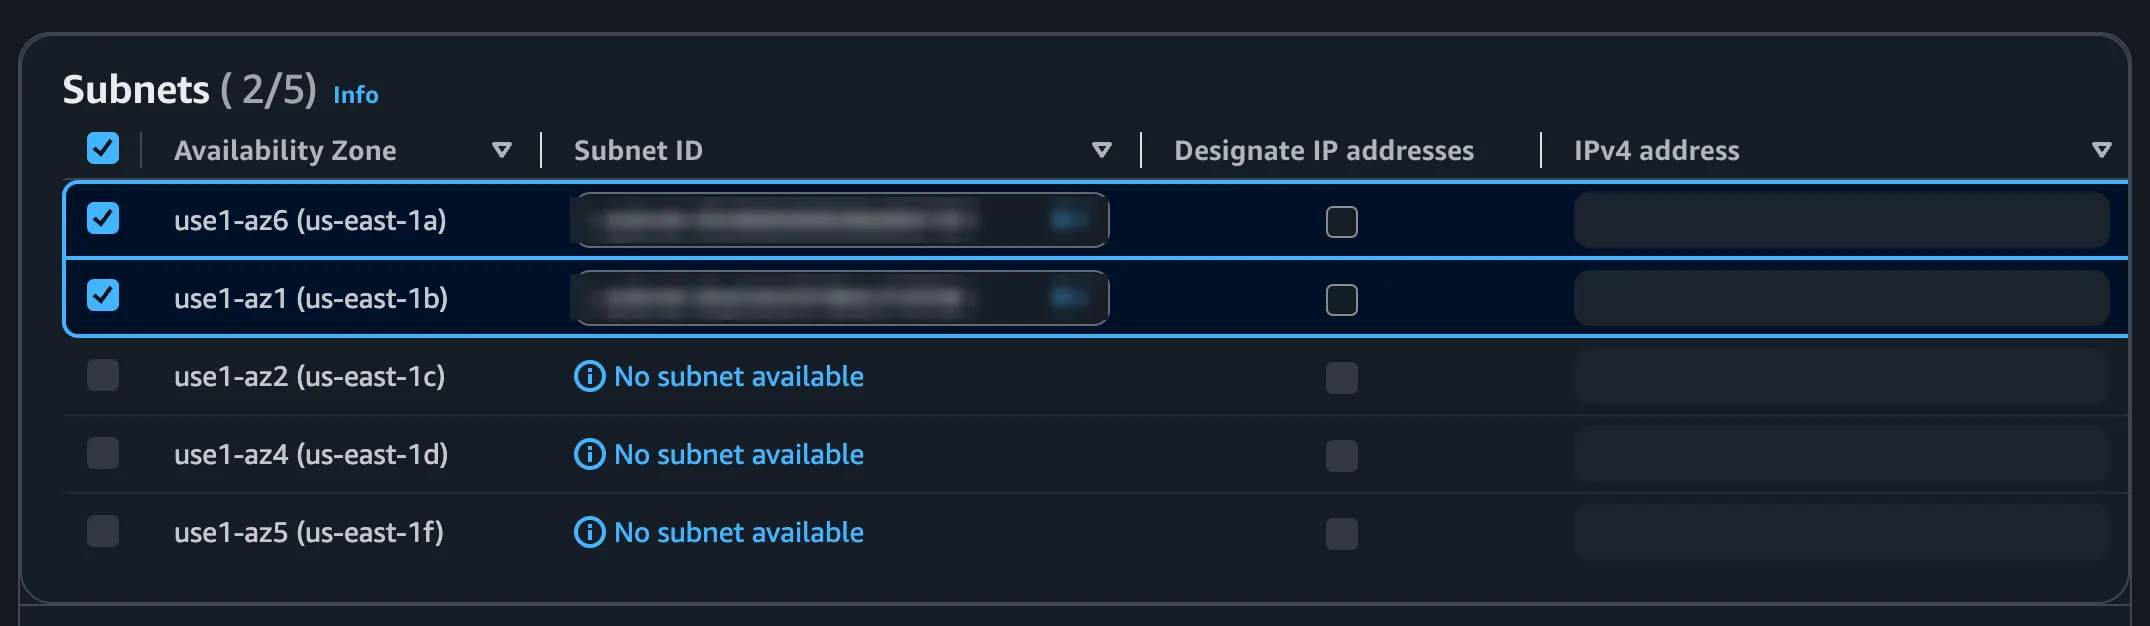
Match on the Availability Zone ID, such as use1-az1, not the Availability Zone name, such as us-east-1a. AWS maps names to physical zones differently in every account, so the same name points to a different zone for you than it does for Tiger Cloud. When you choose subnets, the AWS console shows both in the us-east-1a | use1-az1 form.
Set up a private endpoint connection
Section titled “Set up a private endpoint connection”Take the following steps to connect your Tiger Cloud service to a PrivateLink endpoint.
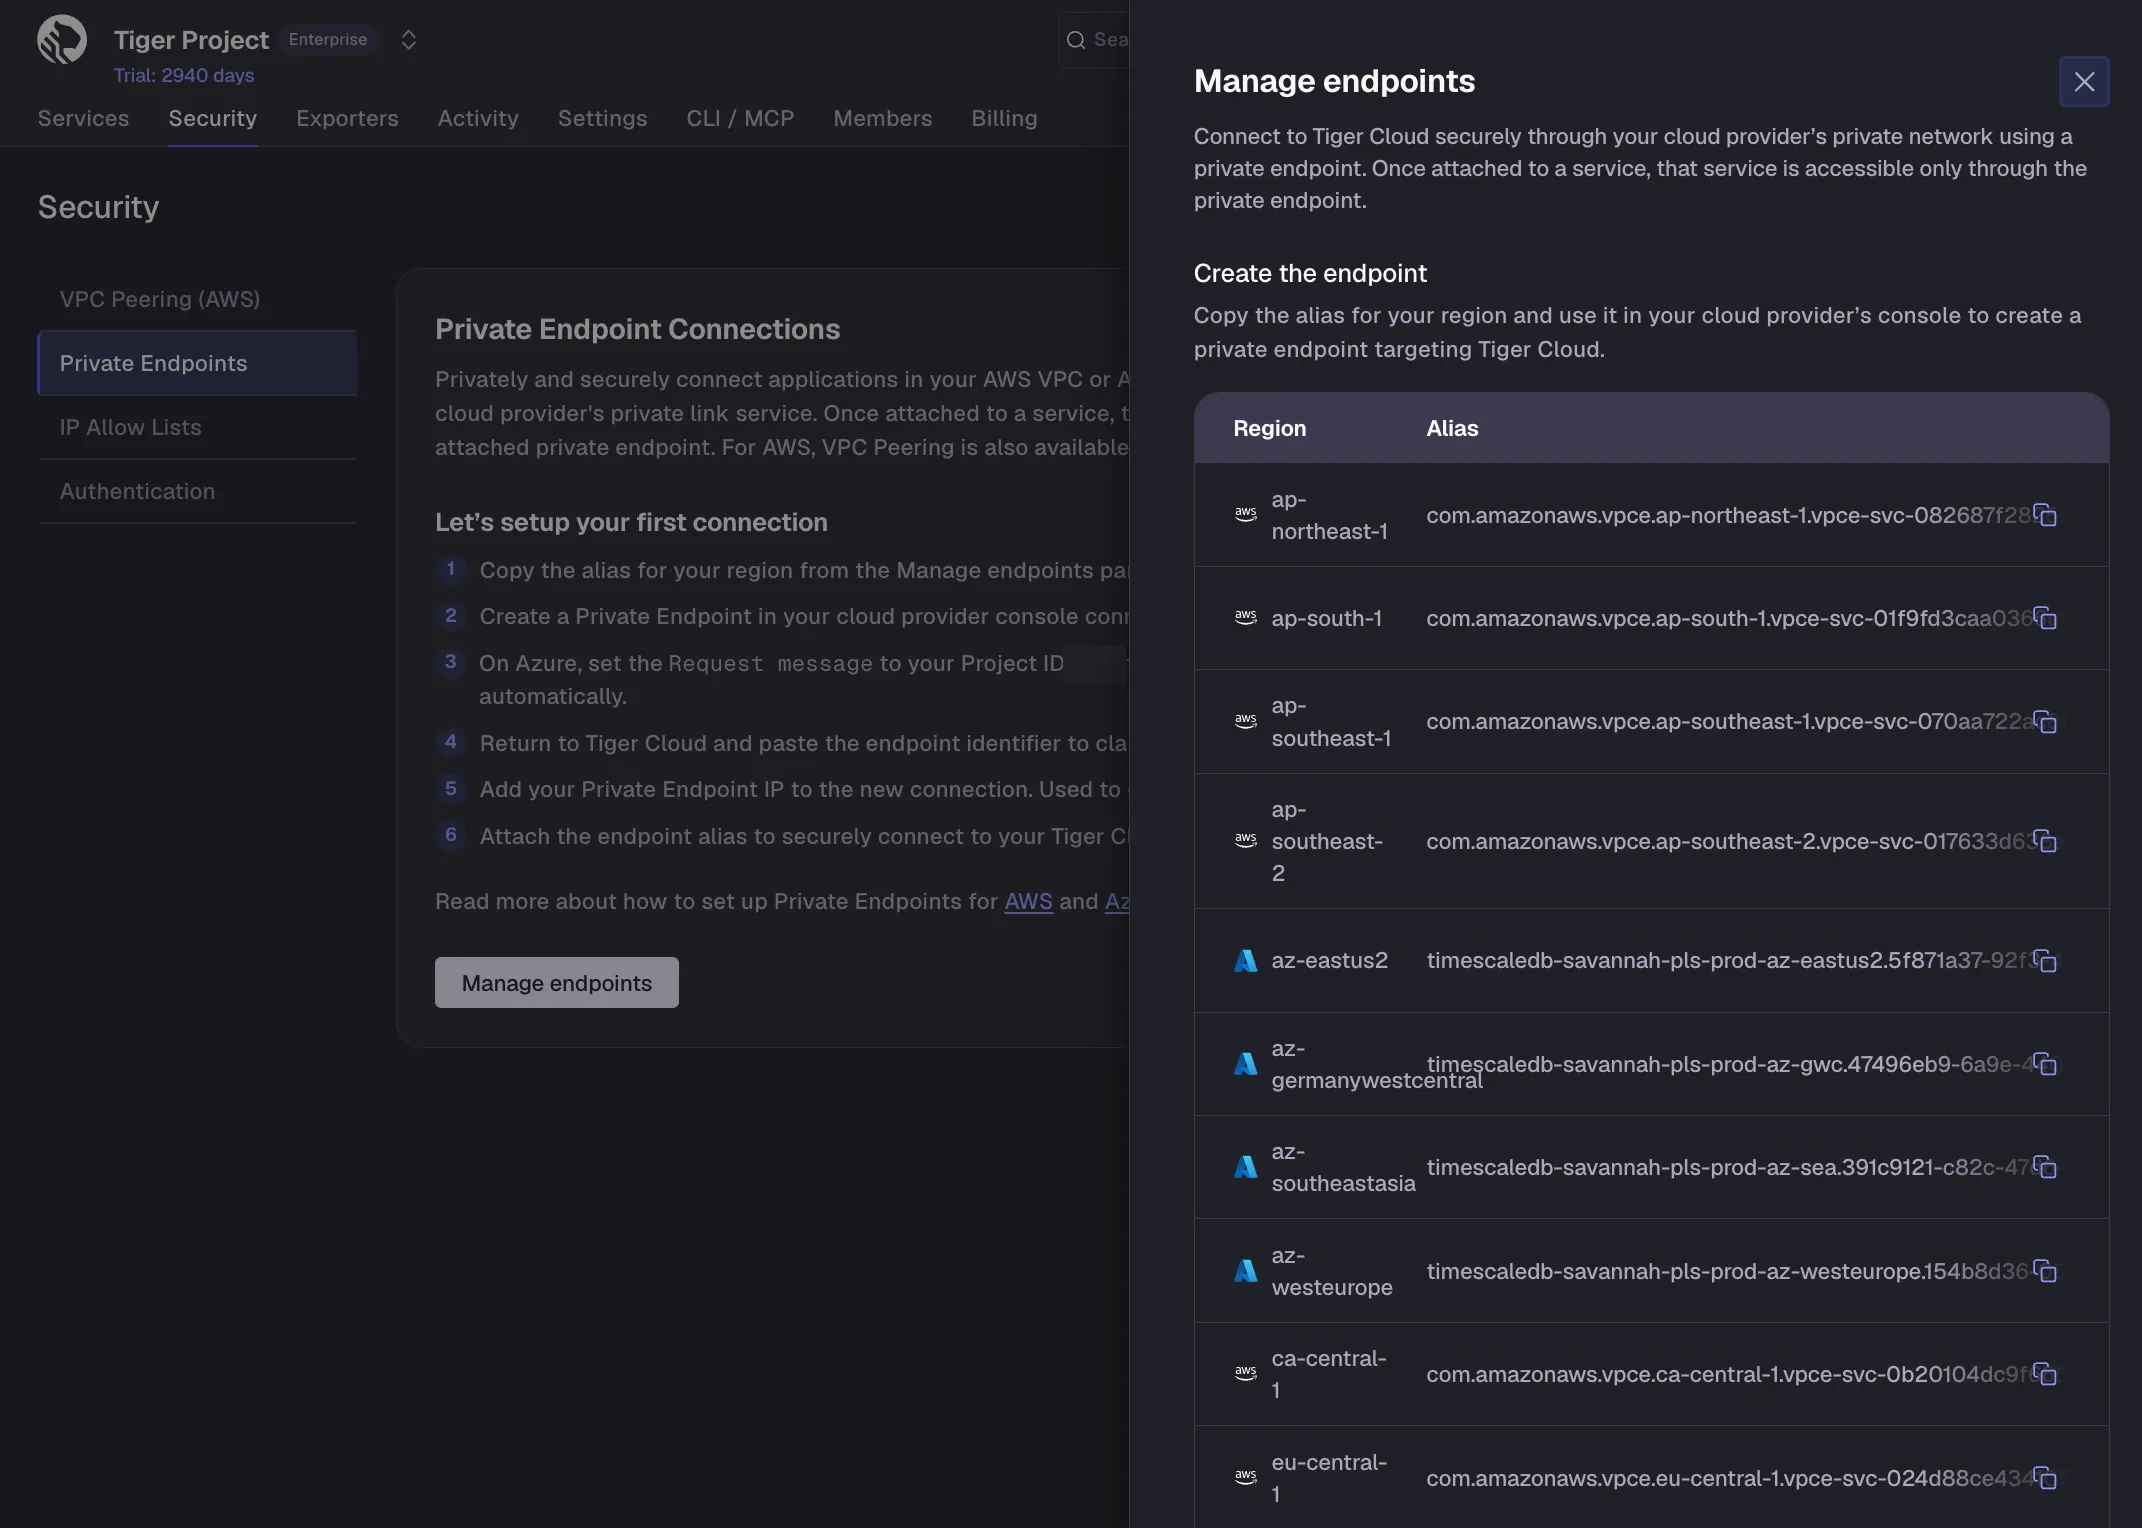
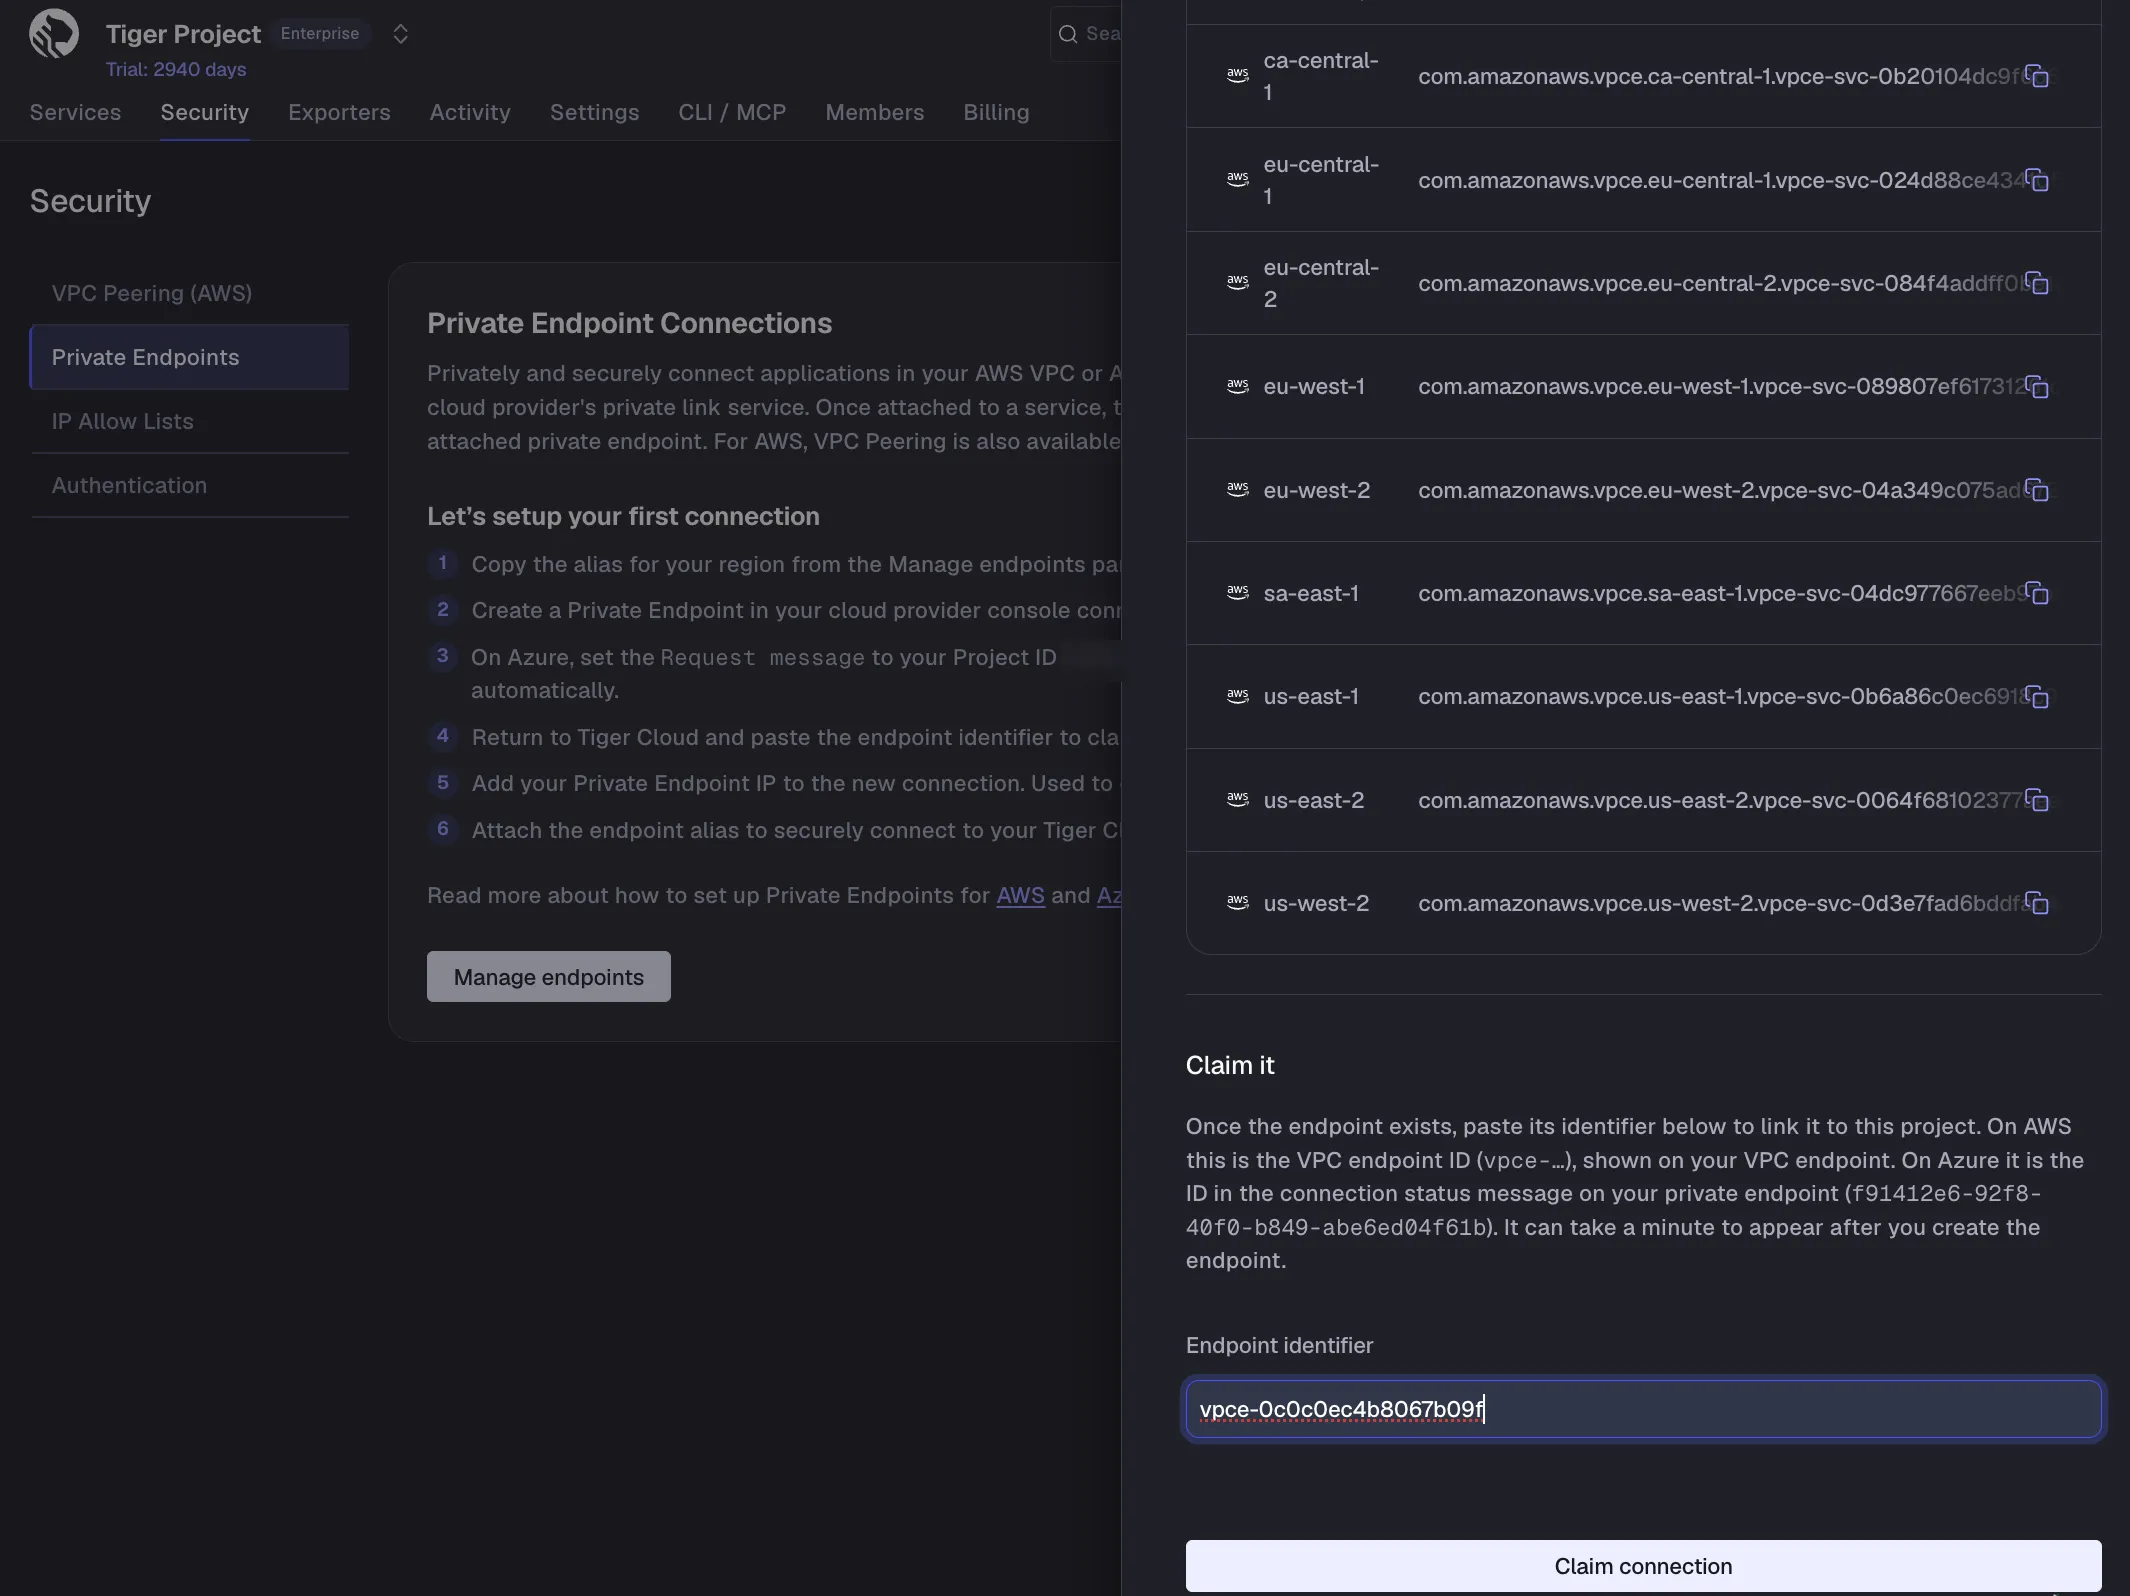
- Copy the alias for your region
-
In Tiger Console, select
Security>Private Endpoints>Manage endpoints. -
Under
Create the endpoint, copy theAliasfor the region in which you need to create the connection. Choose the region of your AWS resources.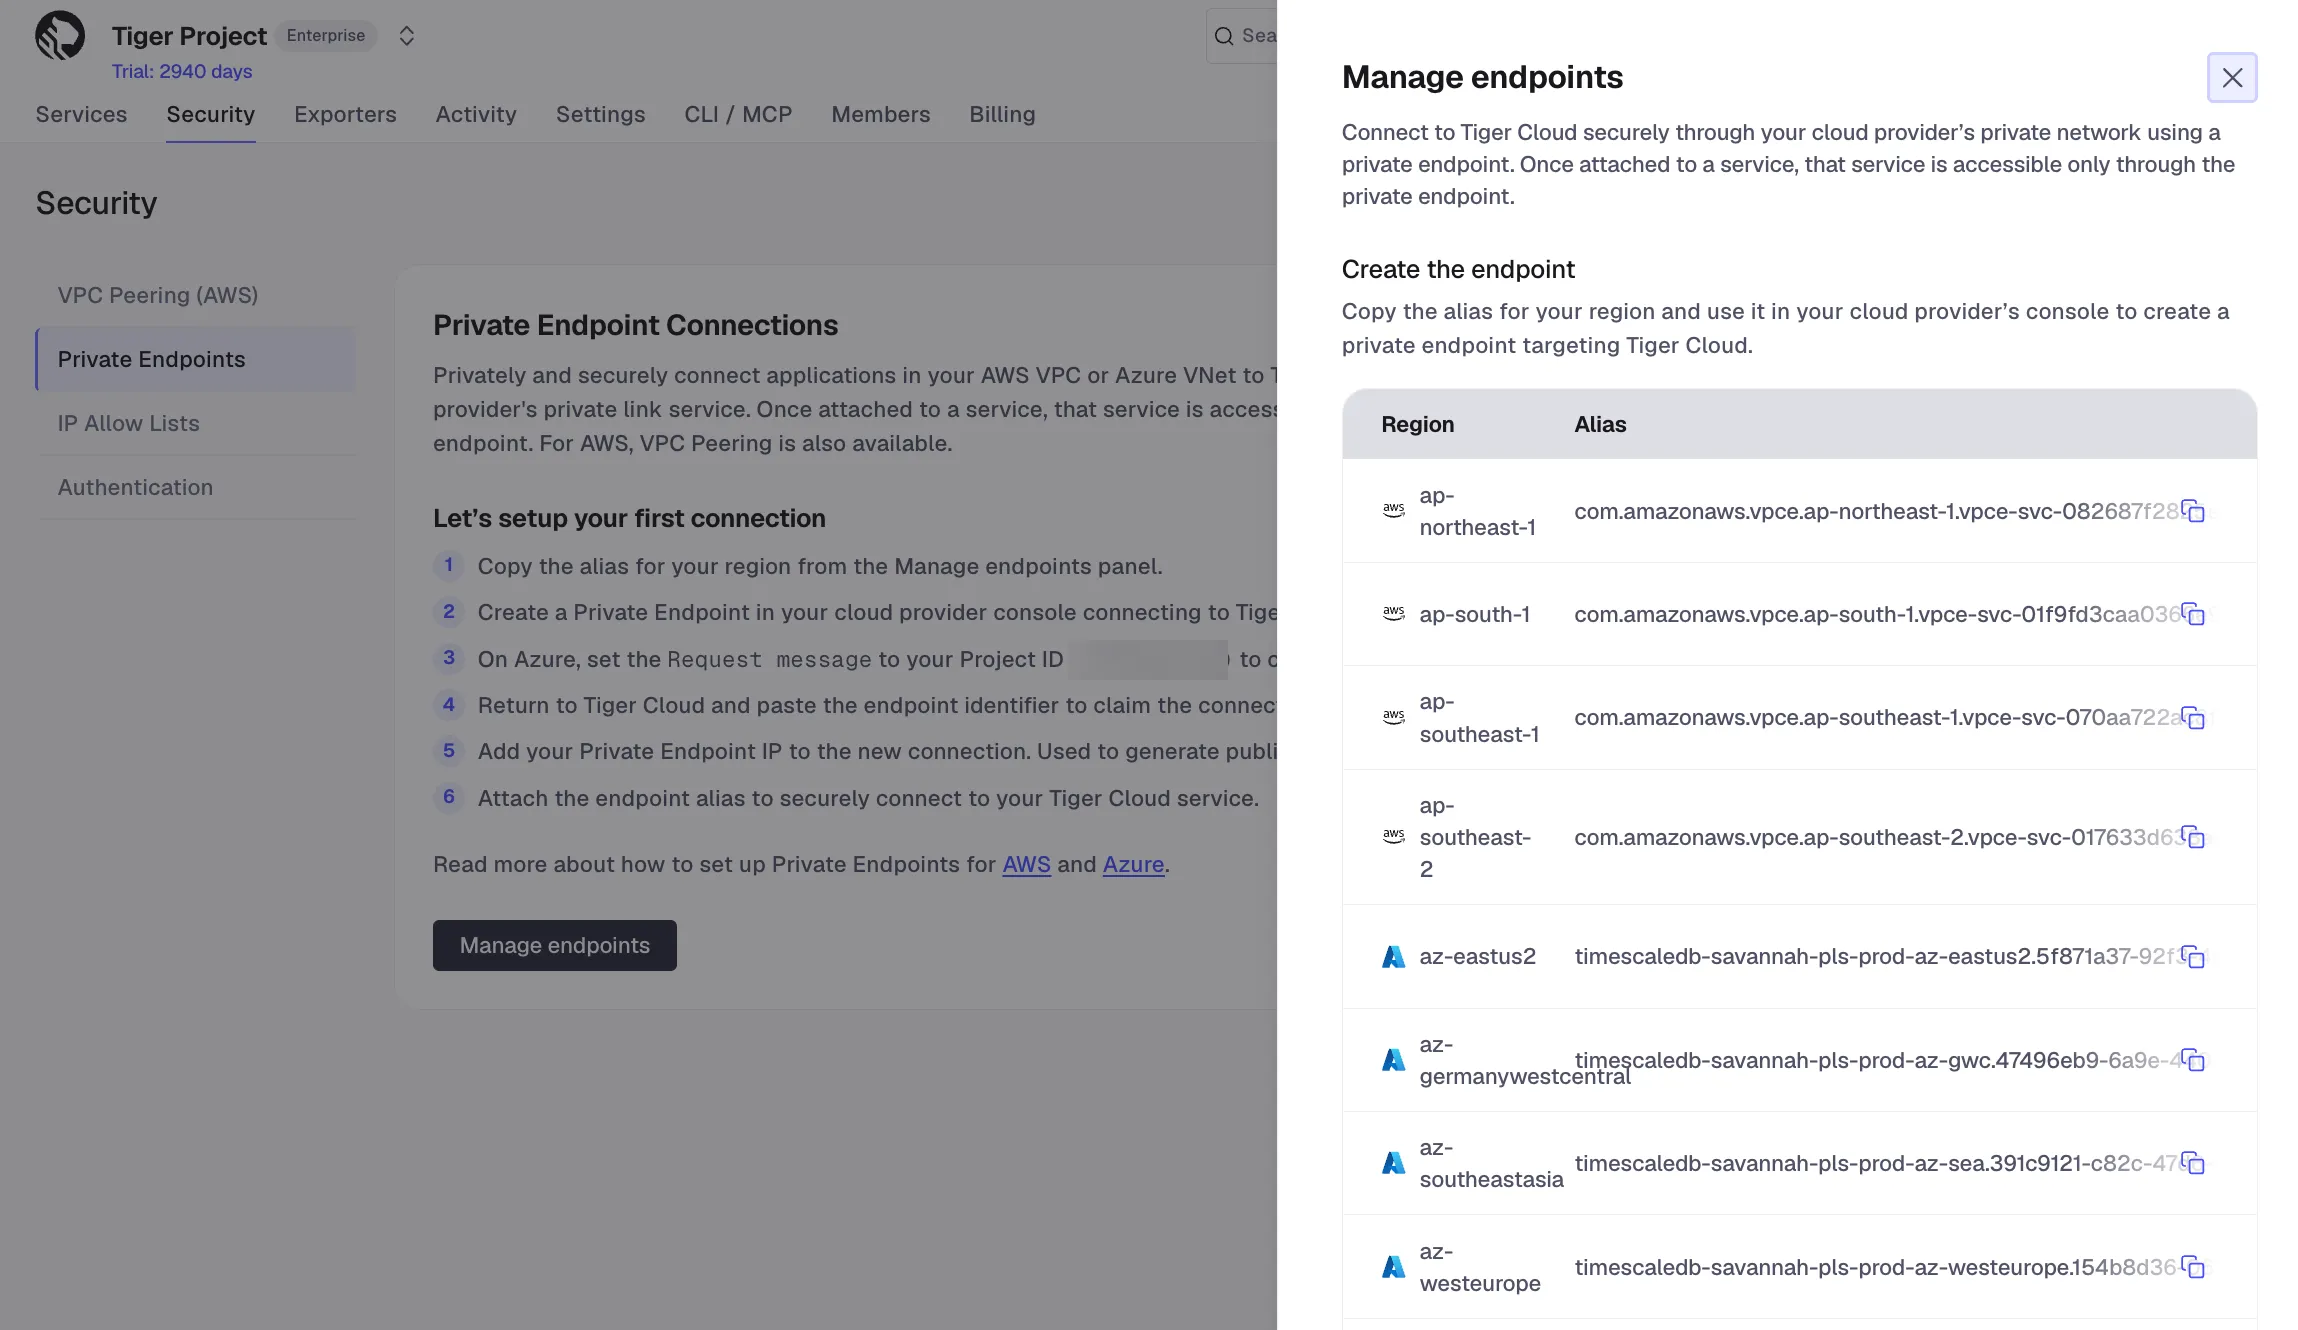
-
- Create a VPC endpoint in AWS
-
In AWS Console, go to
VPC>Endpoints>Create endpoint. -
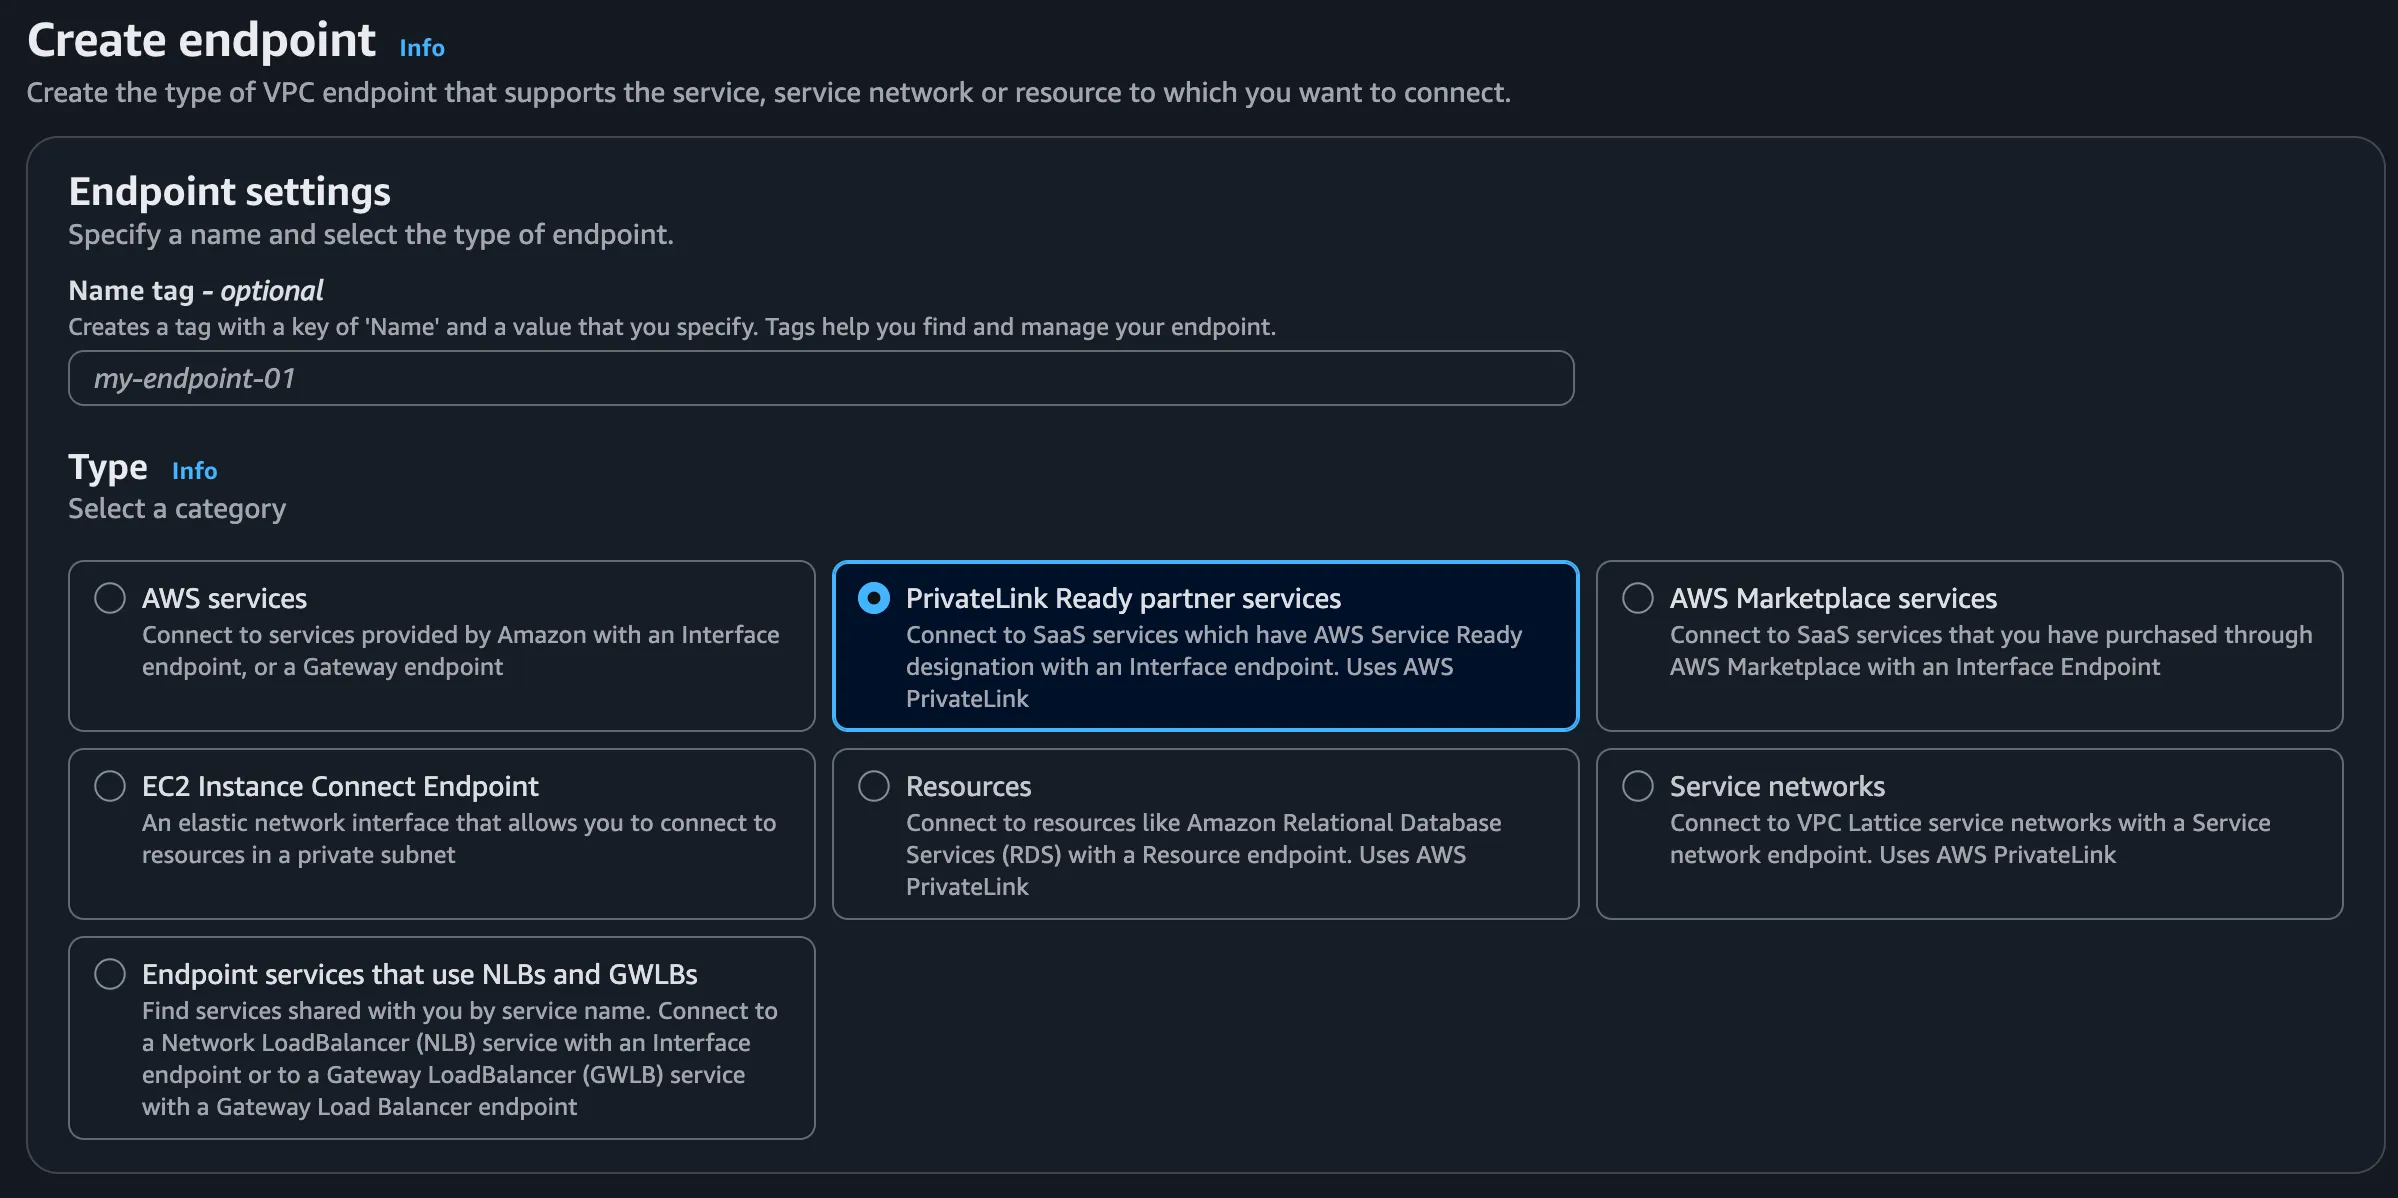
Optionally provide a name tag for your endpoint.
-
Under
Type, selectPrivateLink Ready partner services.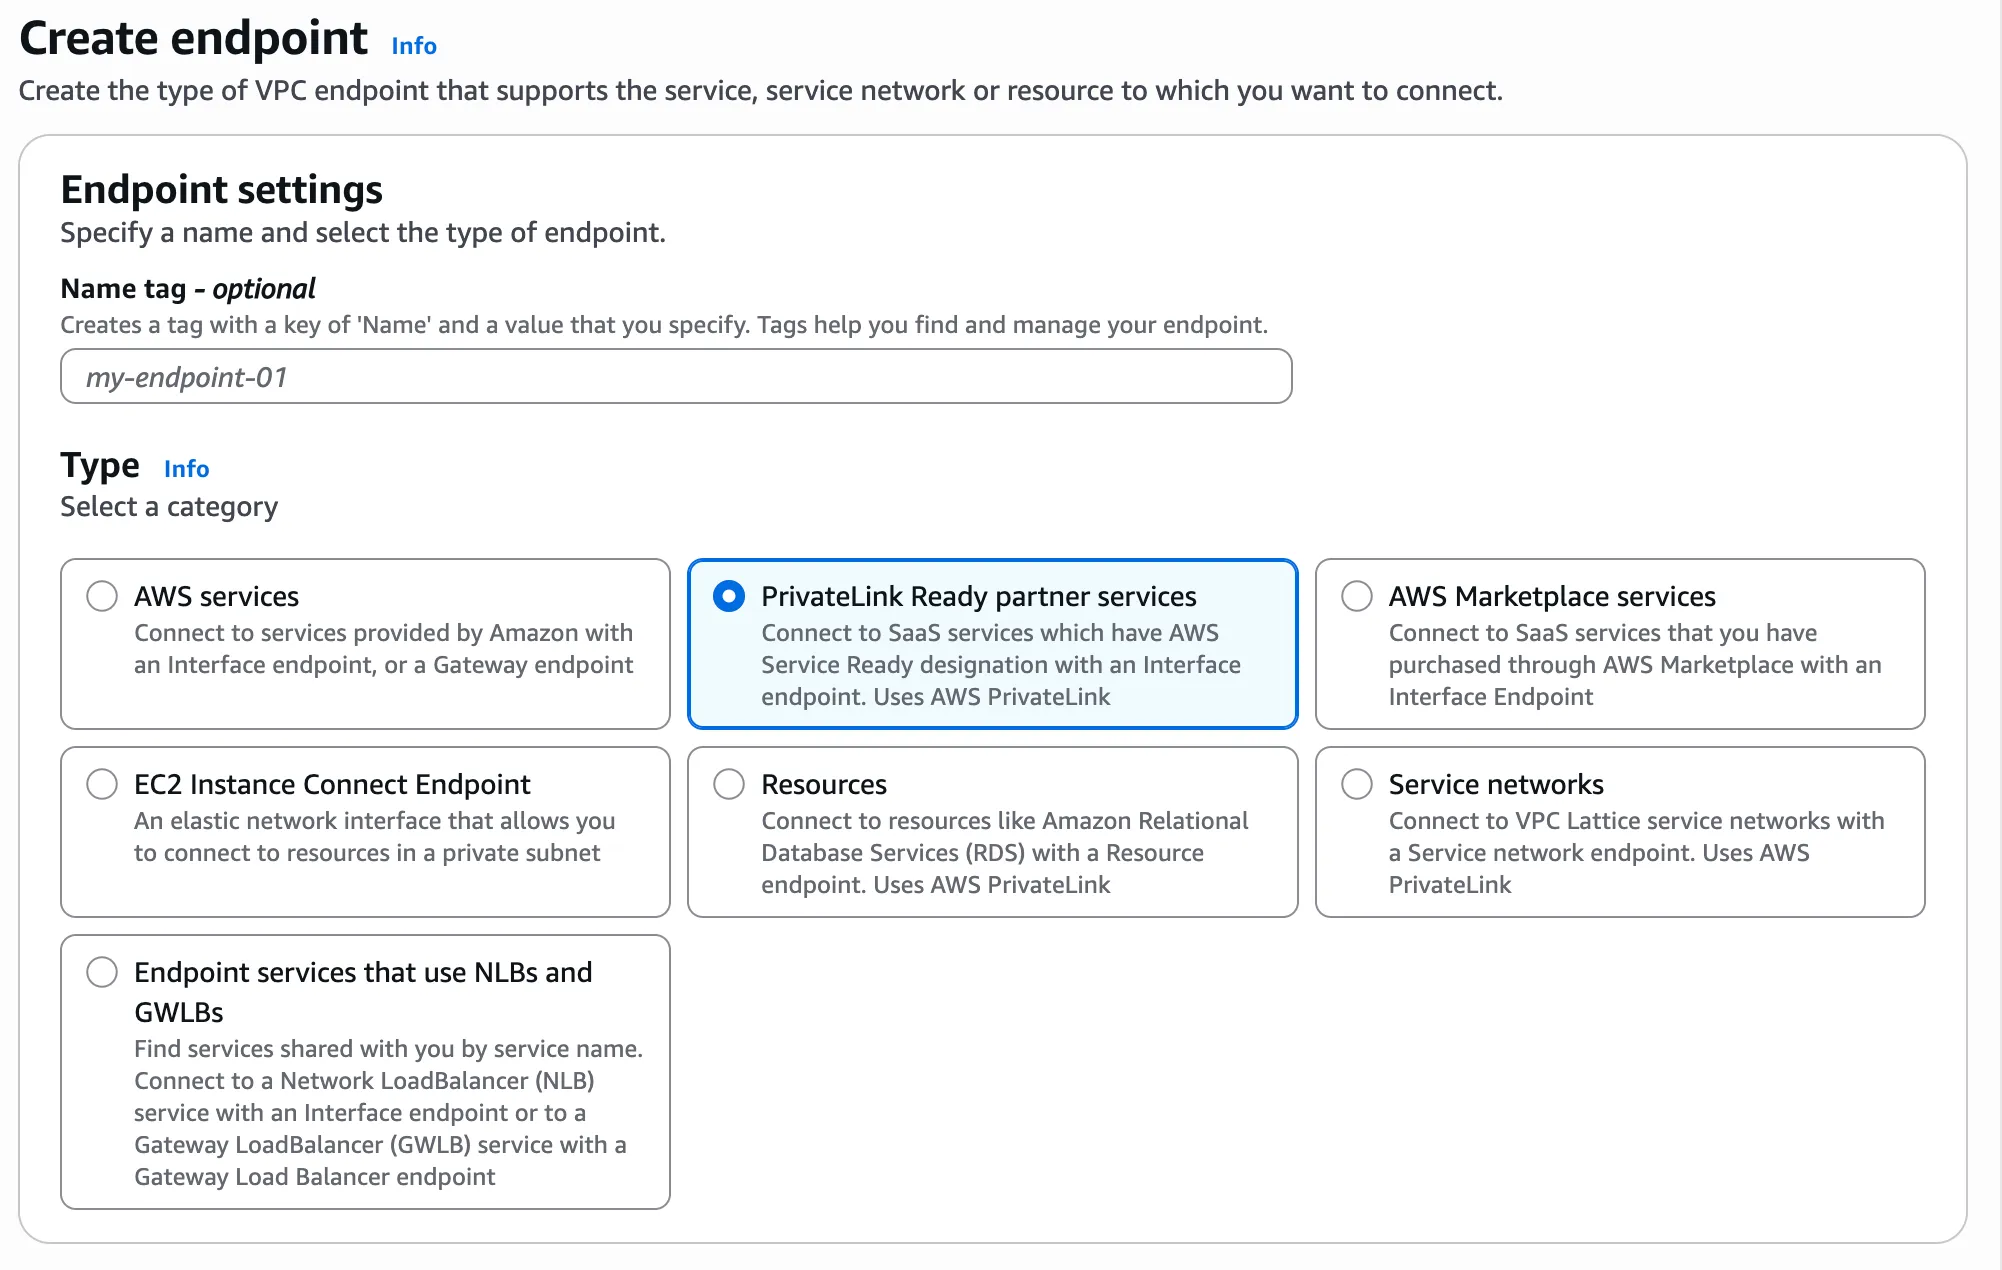
-
Under
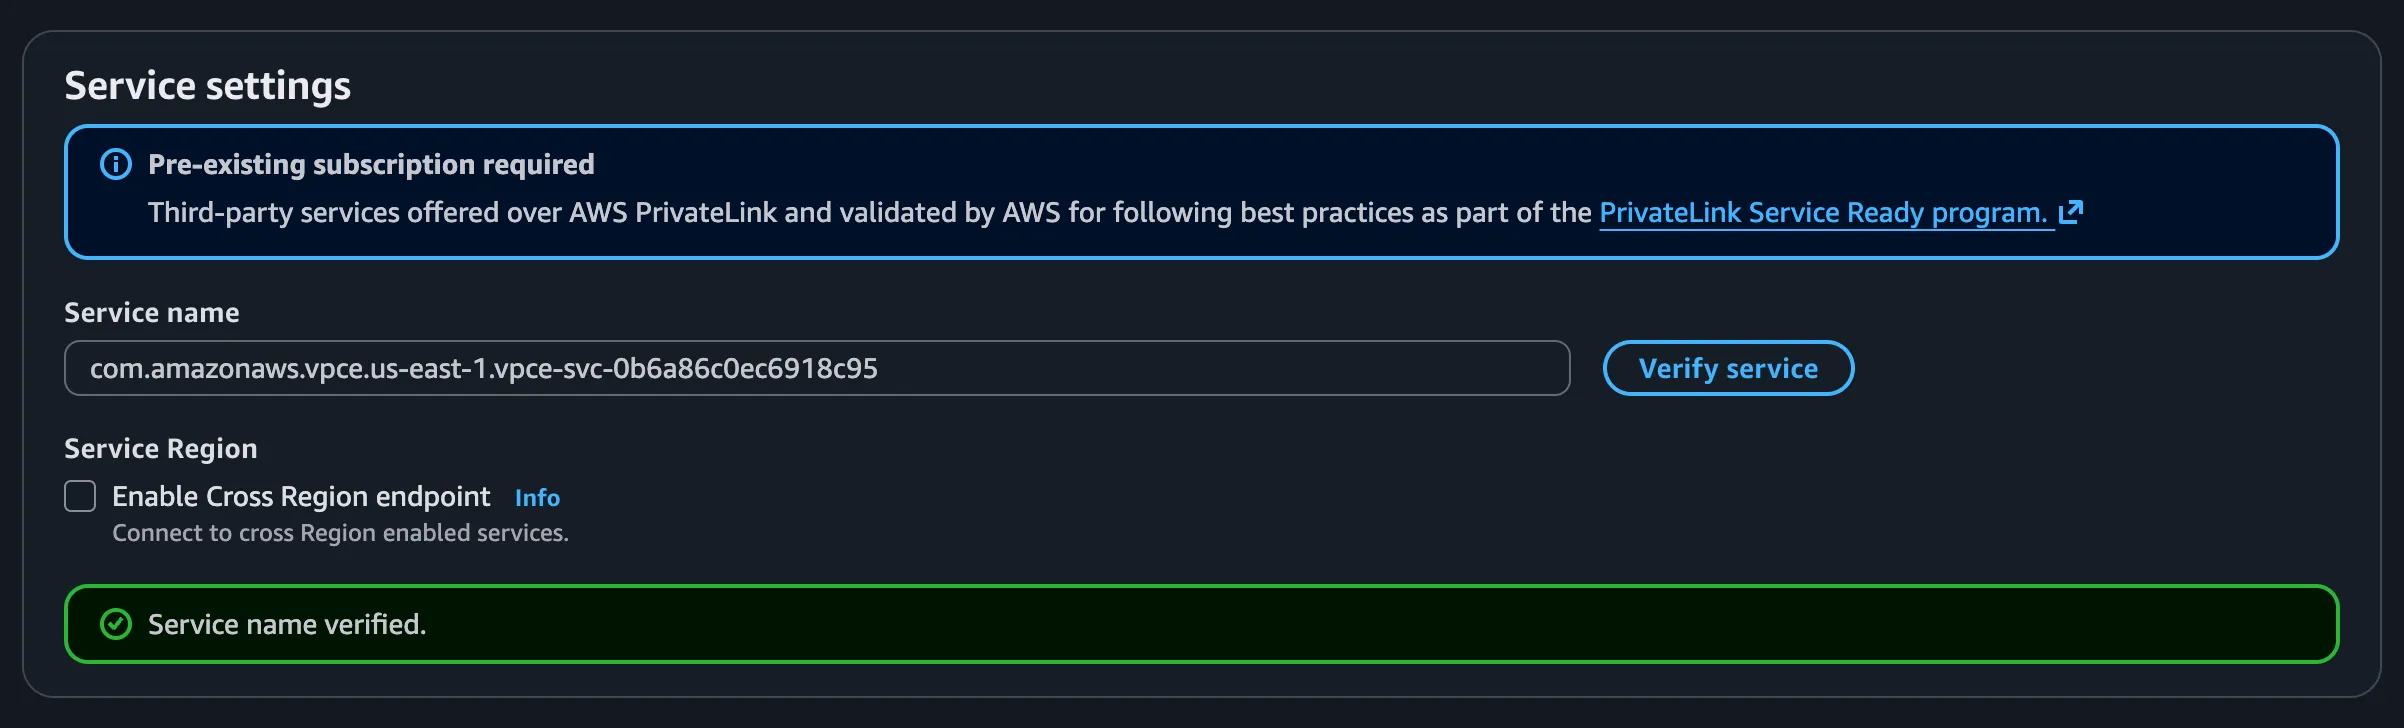
Service settings>Service name, paste in the alias your copied in Tiger Console and clickVerify service. Wait for theService name verified.success message.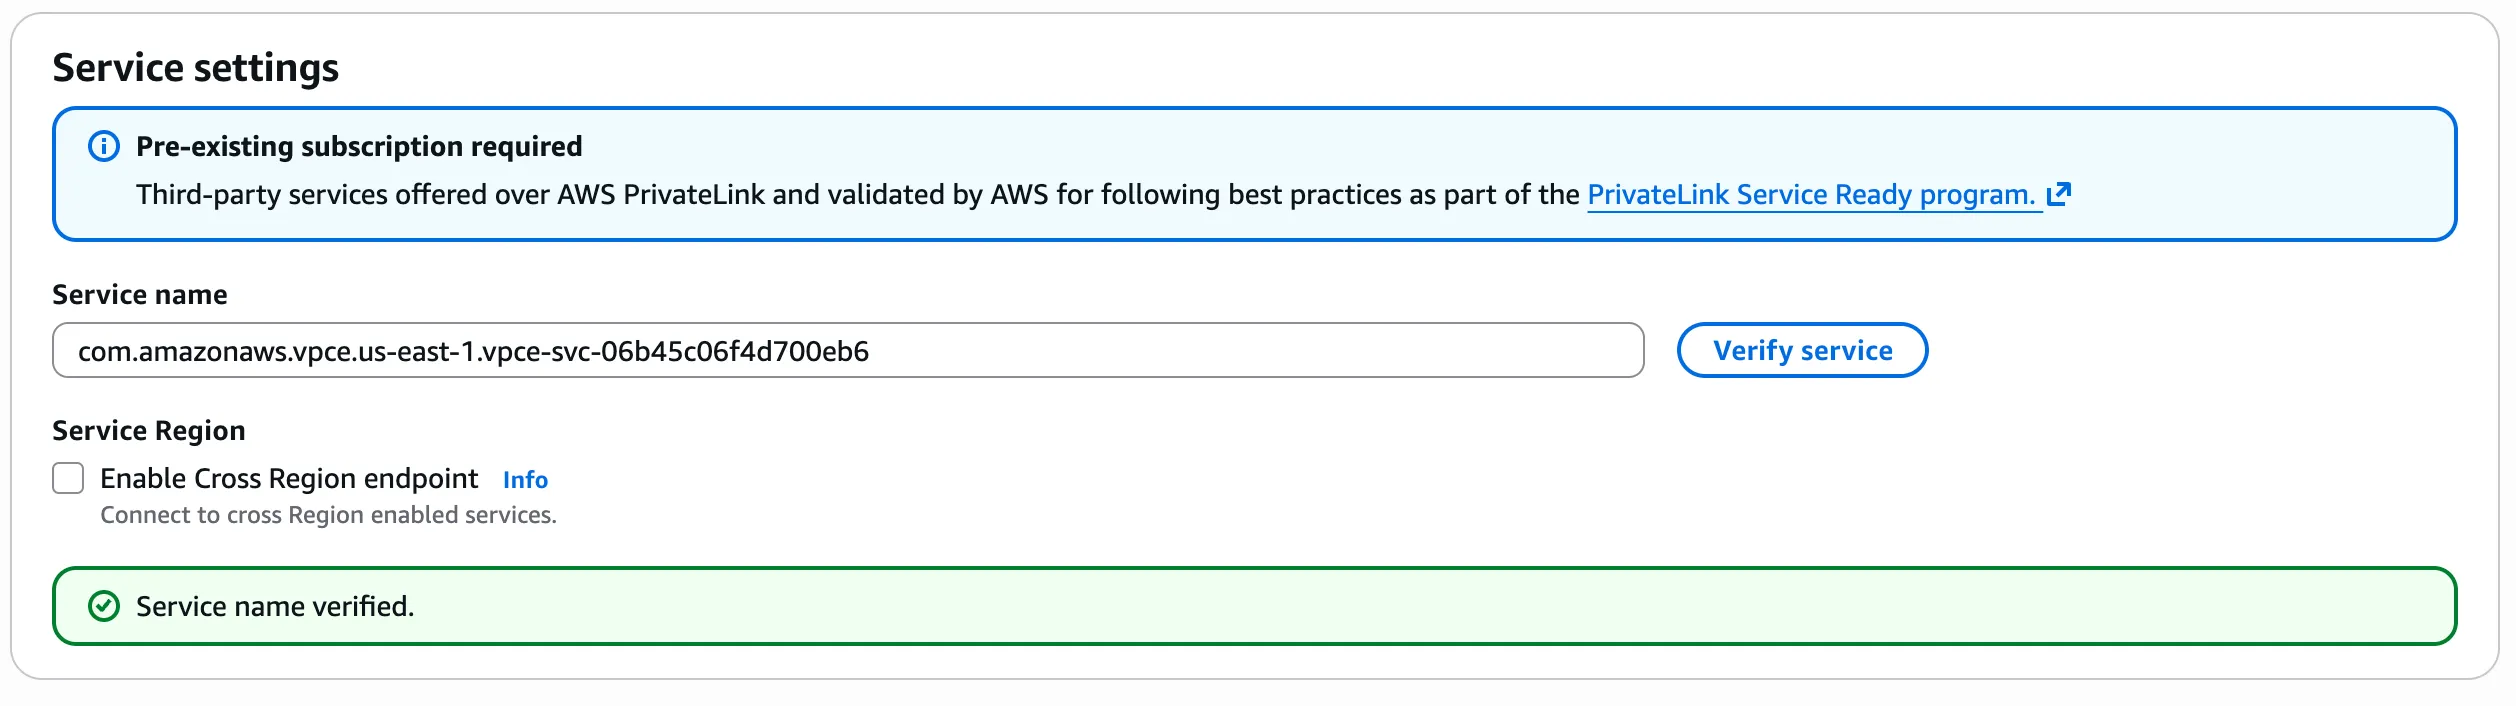
-
Select the VPC that contains the resources you want to connect to Tiger Cloud, then choose the subnets where the endpoint’s private IPs are created. Select a subnet in both of the Availability Zones listed for your region in Availability zones. Selecting only one leaves you without failover, and selecting any other Availability Zone creates an interface that cannot reach your service.
-
Optionally configure the security groups and tags, then click
Create endpoint. -
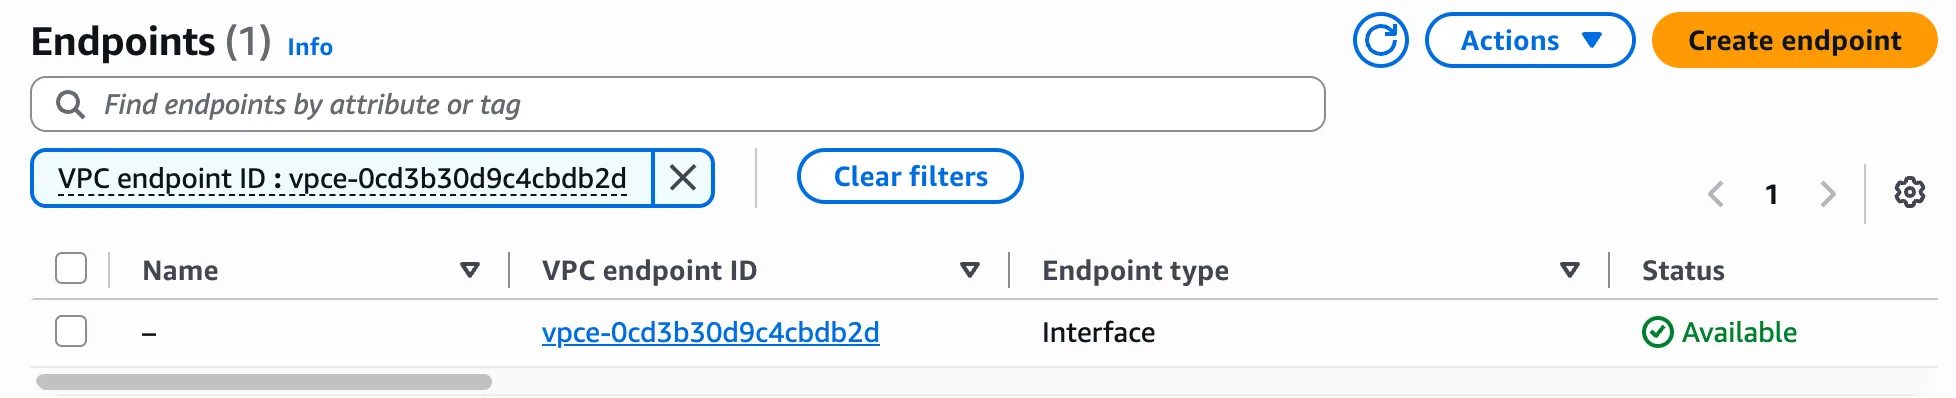
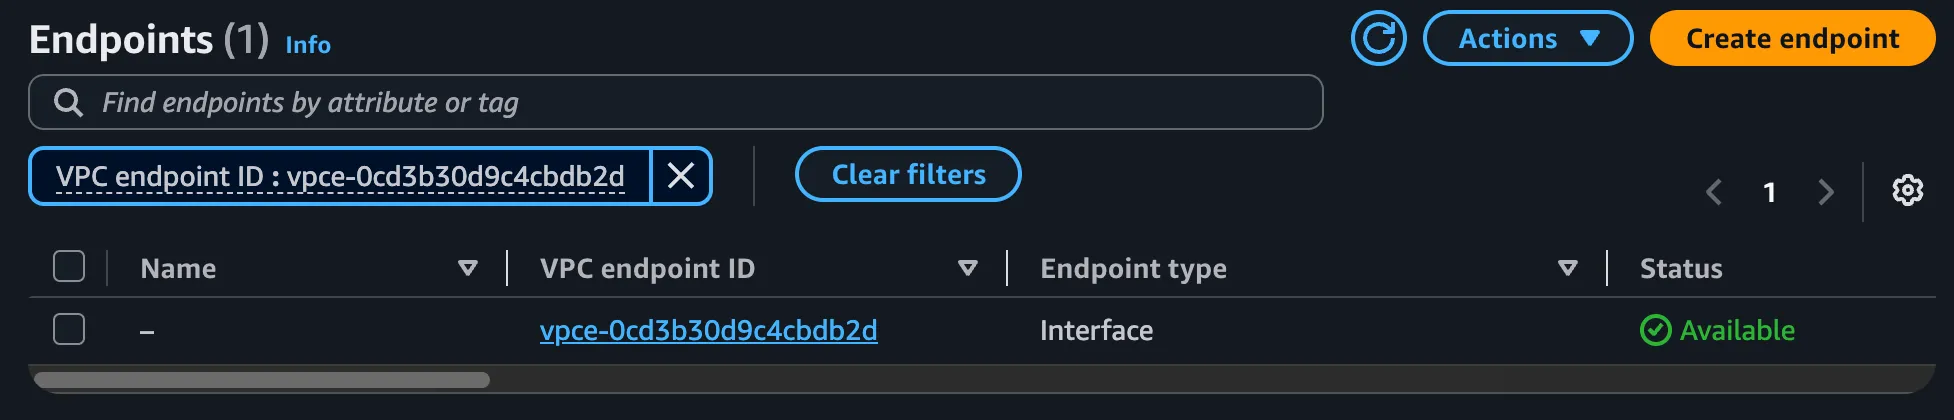
Copy the VPC endpoint ID of your new endpoint. You claim the connection with this ID:
-
- Claim the connection
-
In Tiger Console >
Security>Private Endpoints, clickManage endpoints. -
Under
Claim it, paste your VPC endpoint ID intoEndpoint identifier, then clickClaim connection. Tiger Cloud links the connection to the project you are working in, and it appears in the list.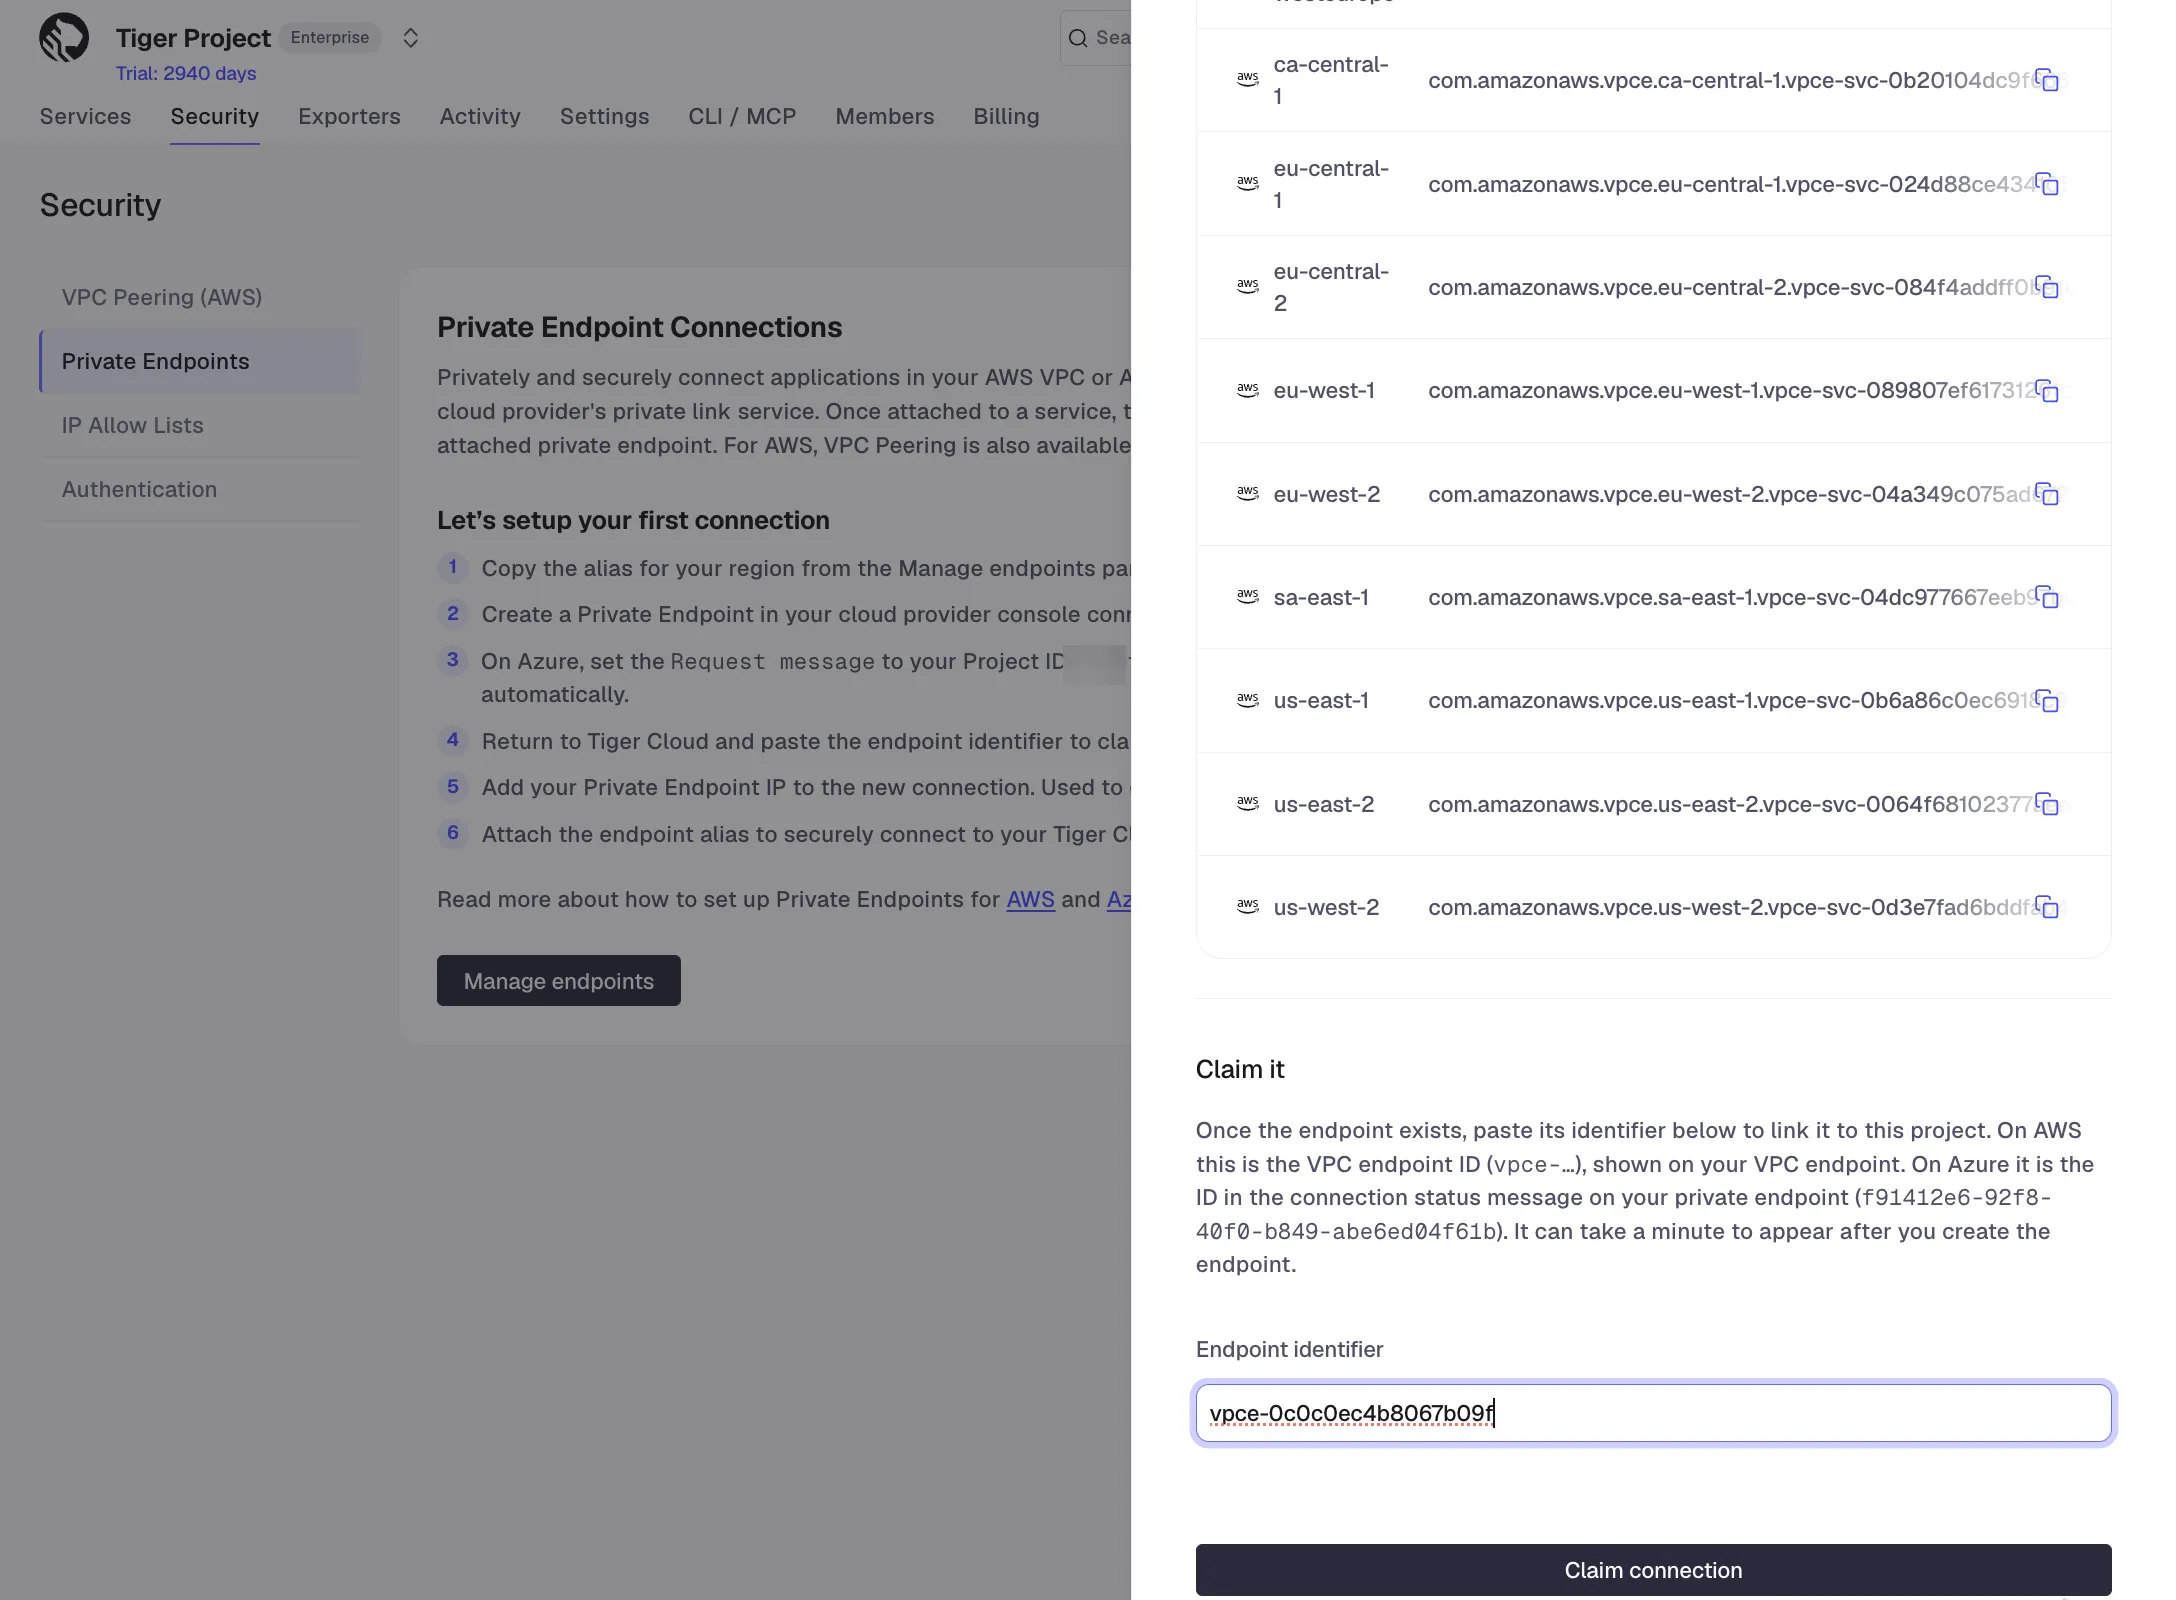 Note
You can claim a VPC endpoint against one project only.
Your VPC endpoint ID can also take a minute to become claimable after you create the endpoint in AWS.
-
- Attach a service
Under
ServicesclickAttach service. Select your service from the dropdown and clickAttach. You can attach a service to one private endpoint. - Publish the service hostname in your private DNS
You resolve your service hostname to your VPC endpoint in a private hosted zone that you control.
-
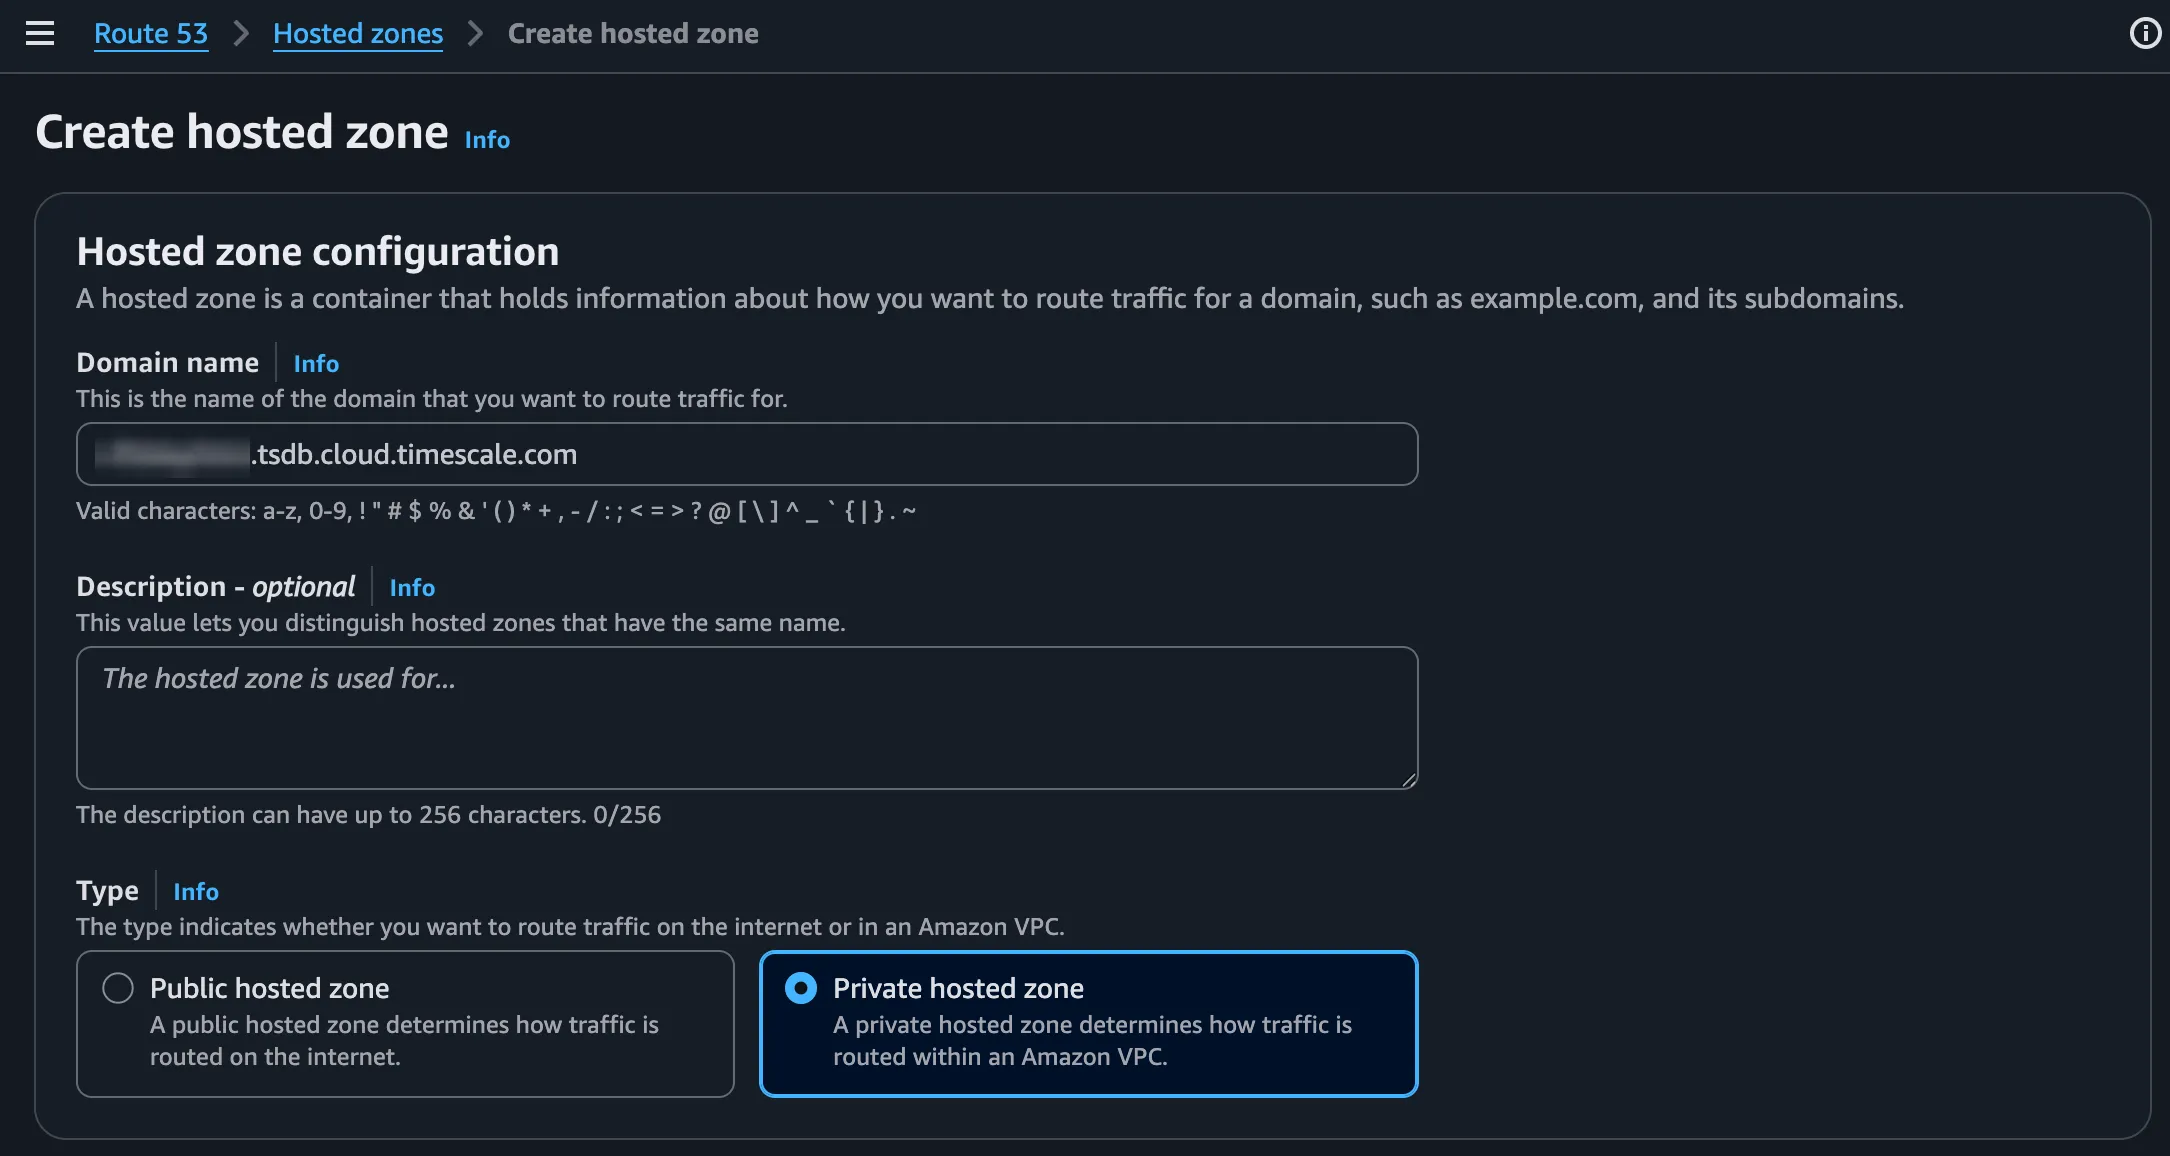
In Route 53, create a private hosted zone for
<project-id>.tsdb.cloud.timescale.com. SetTypetoPrivate hosted zone.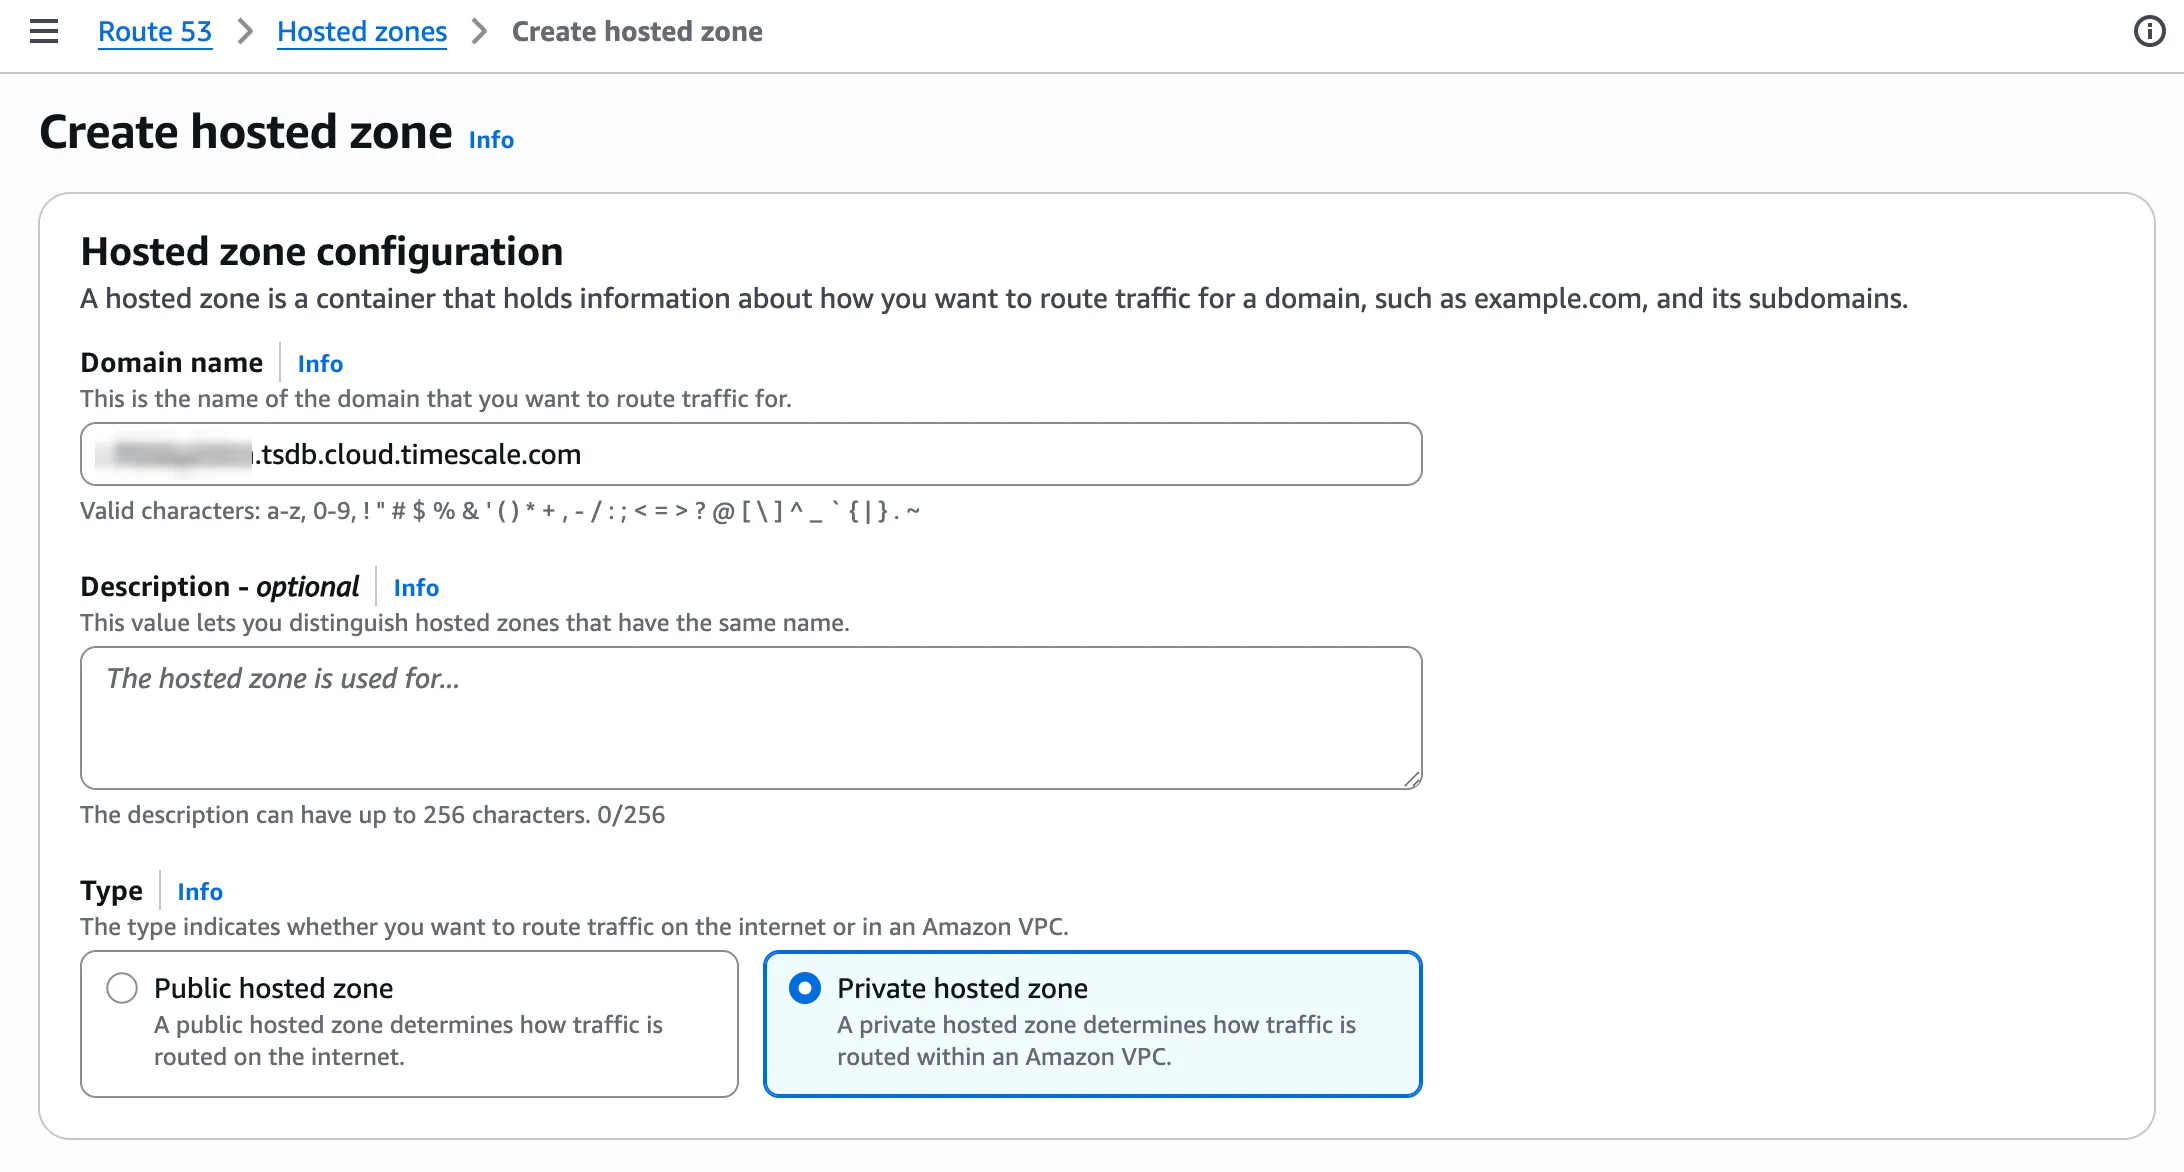
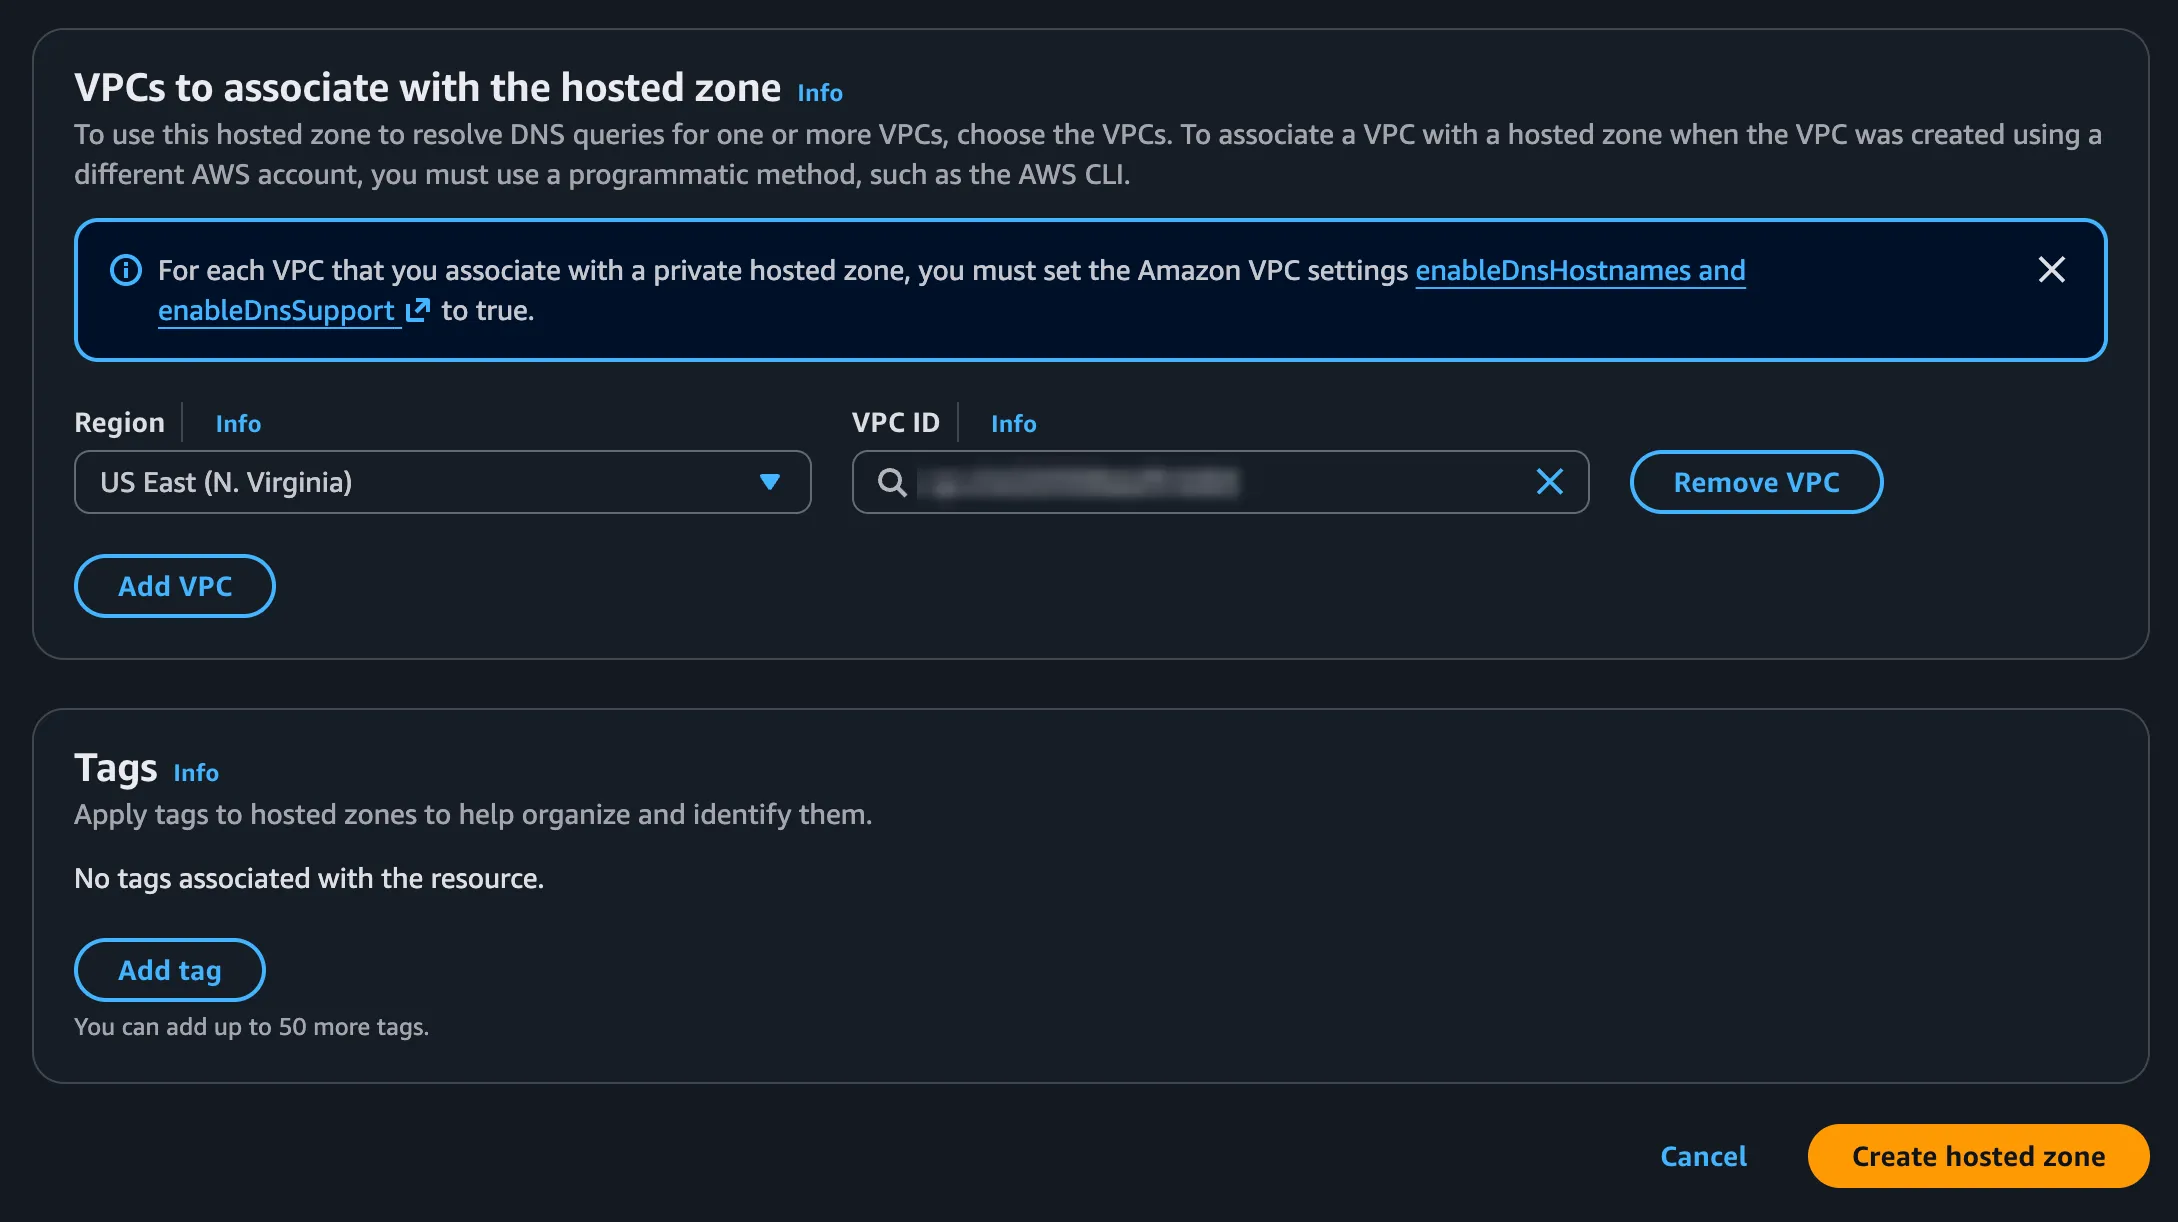
Under
VPCs to associate with the hosted zone, select the region and the VPC that contains your resources. If you already have a private hosted zone for this domain, use it instead of creating another.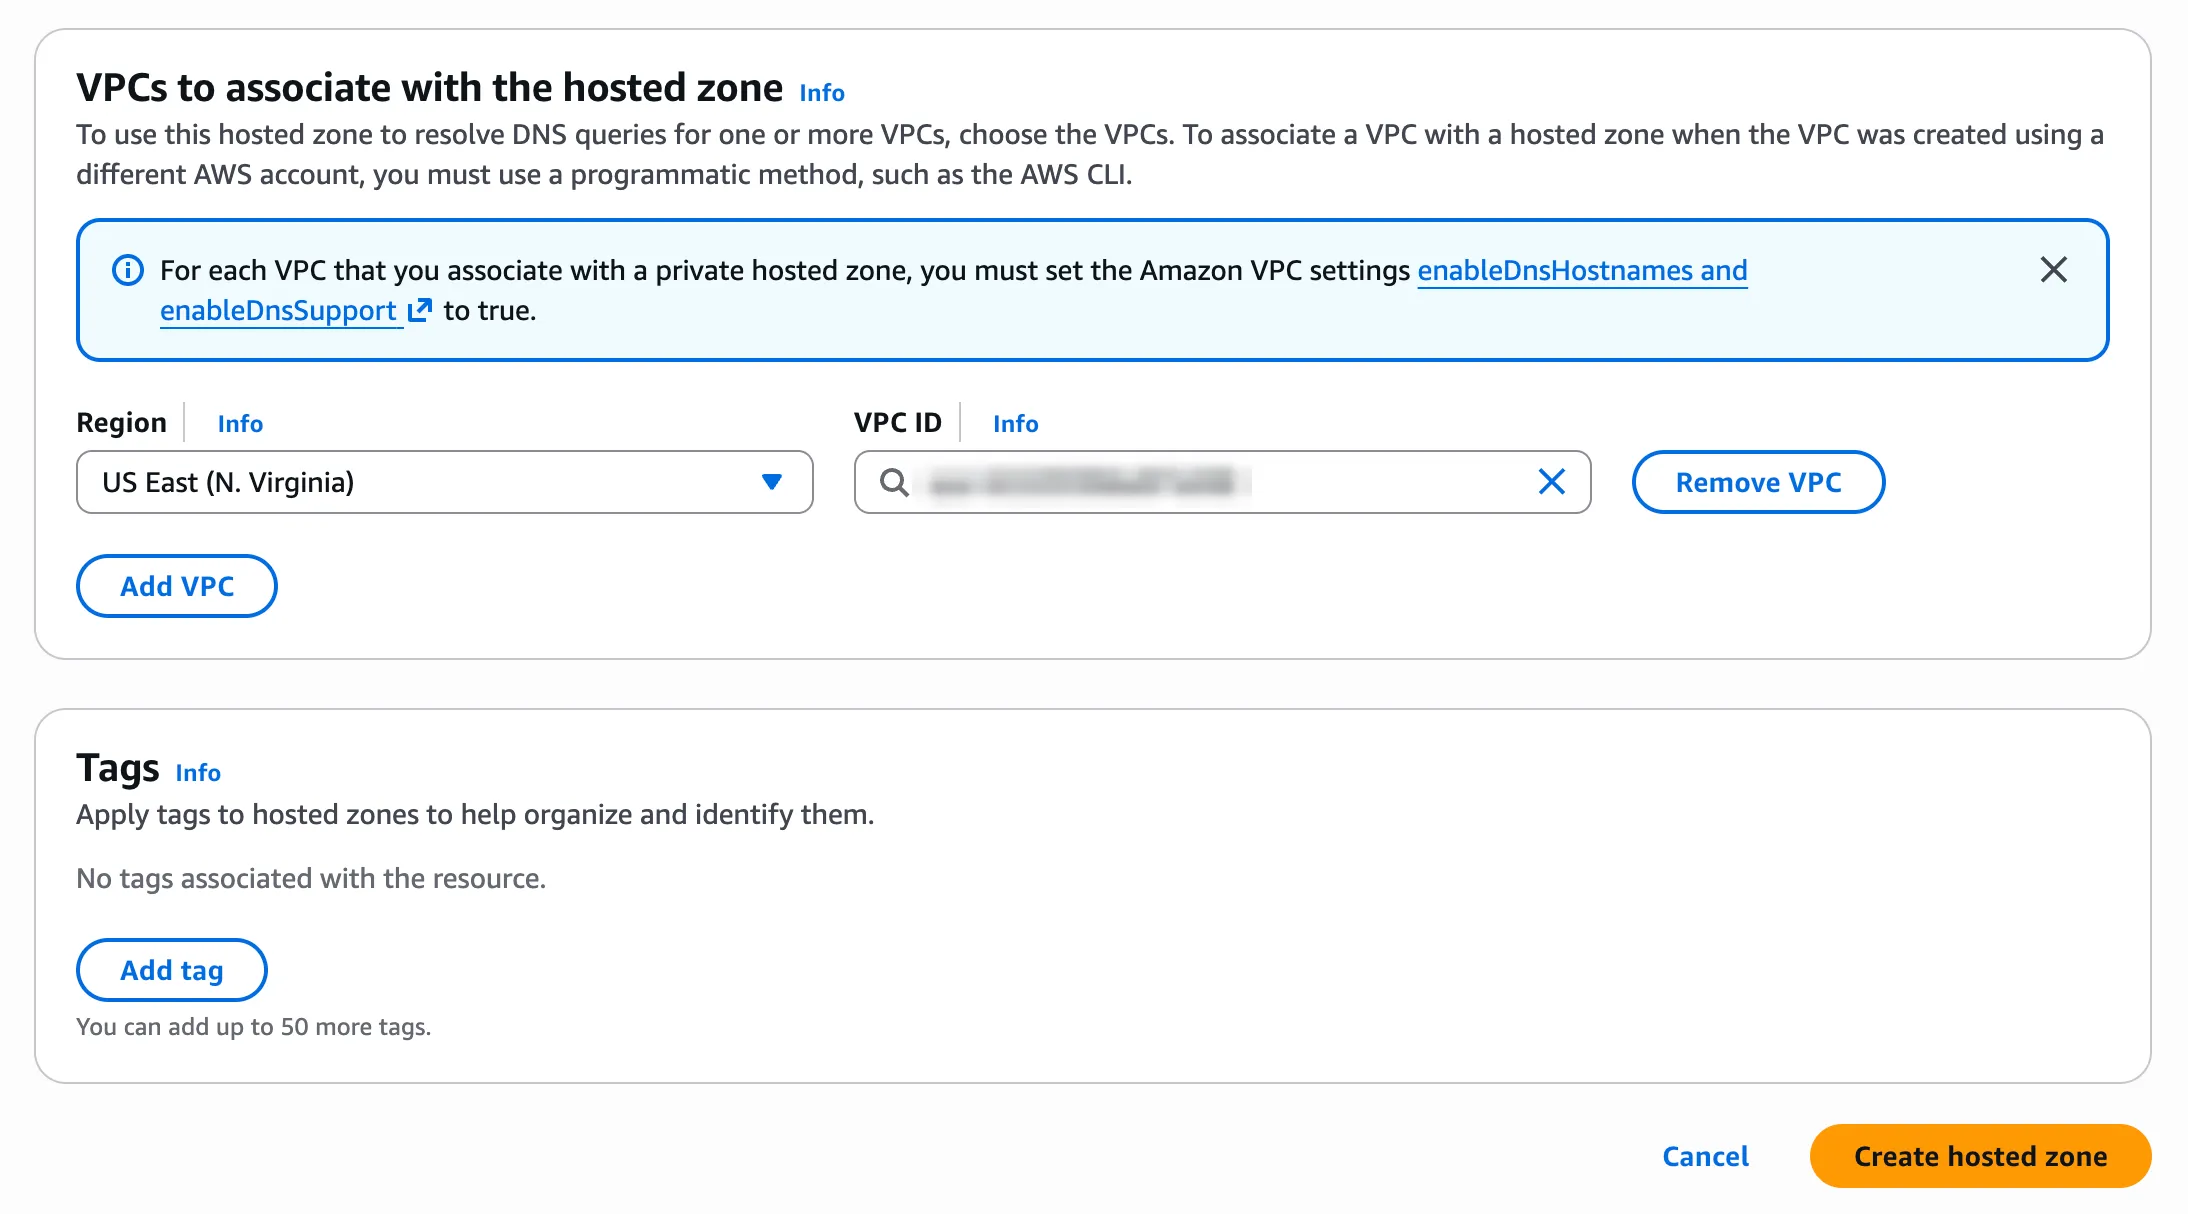
-
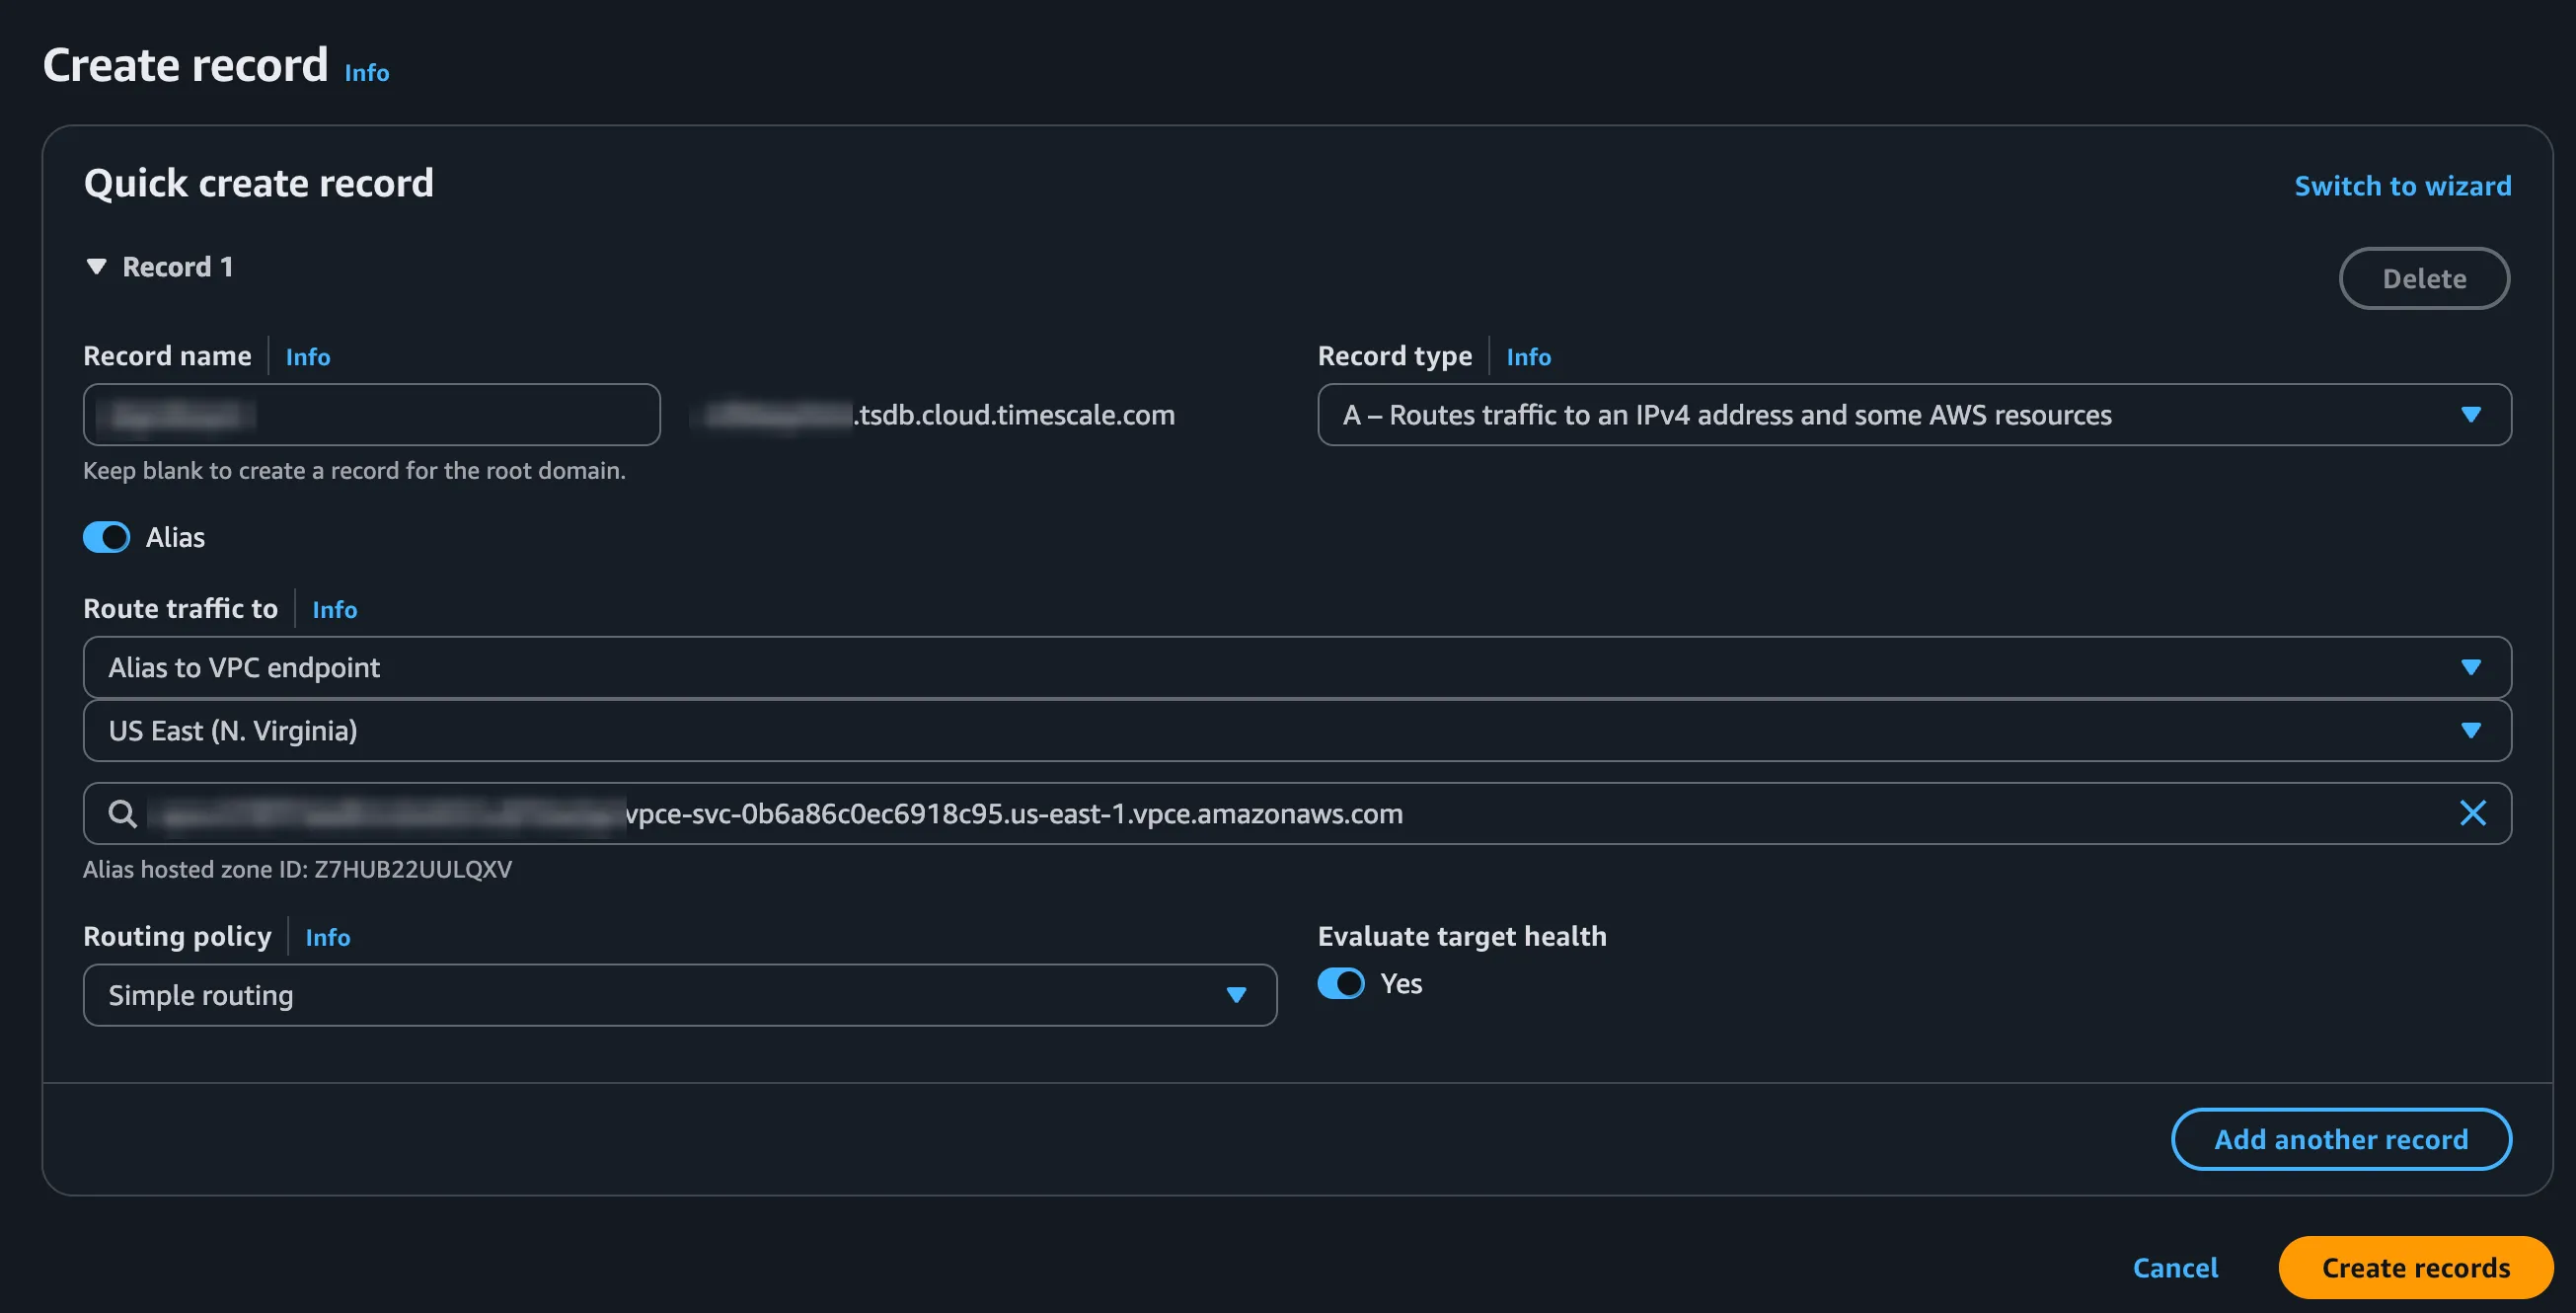
In that zone, create a record for your service hostname,
<service-id>.<project-id>.tsdb.cloud.timescale.com. Create anArecord, enableAlias, chooseAlias to VPC endpoint, then select your region. An alias record resolves in a single step and Route 53 does not charge for queries to it, so prefer it over aCNAME.The endpoint dropdown lists three names for your endpoint: one regional and one for each Availability Zone. Select the regional name, which has no Availability Zone in it:
vpce-<id>-<hash>.vpce-svc-<id>.<region>.vpce.amazonaws.comThe zonal names carry the Availability Zone just before
.vpce-svc-, as invpce-<id>-<hash>-us-east-1a.vpce-svc-<id>.... The regional name resolves across every healthy interface, so traffic fails over if an Availability Zone goes down. A zonal name pins traffic to one zone and fails with it.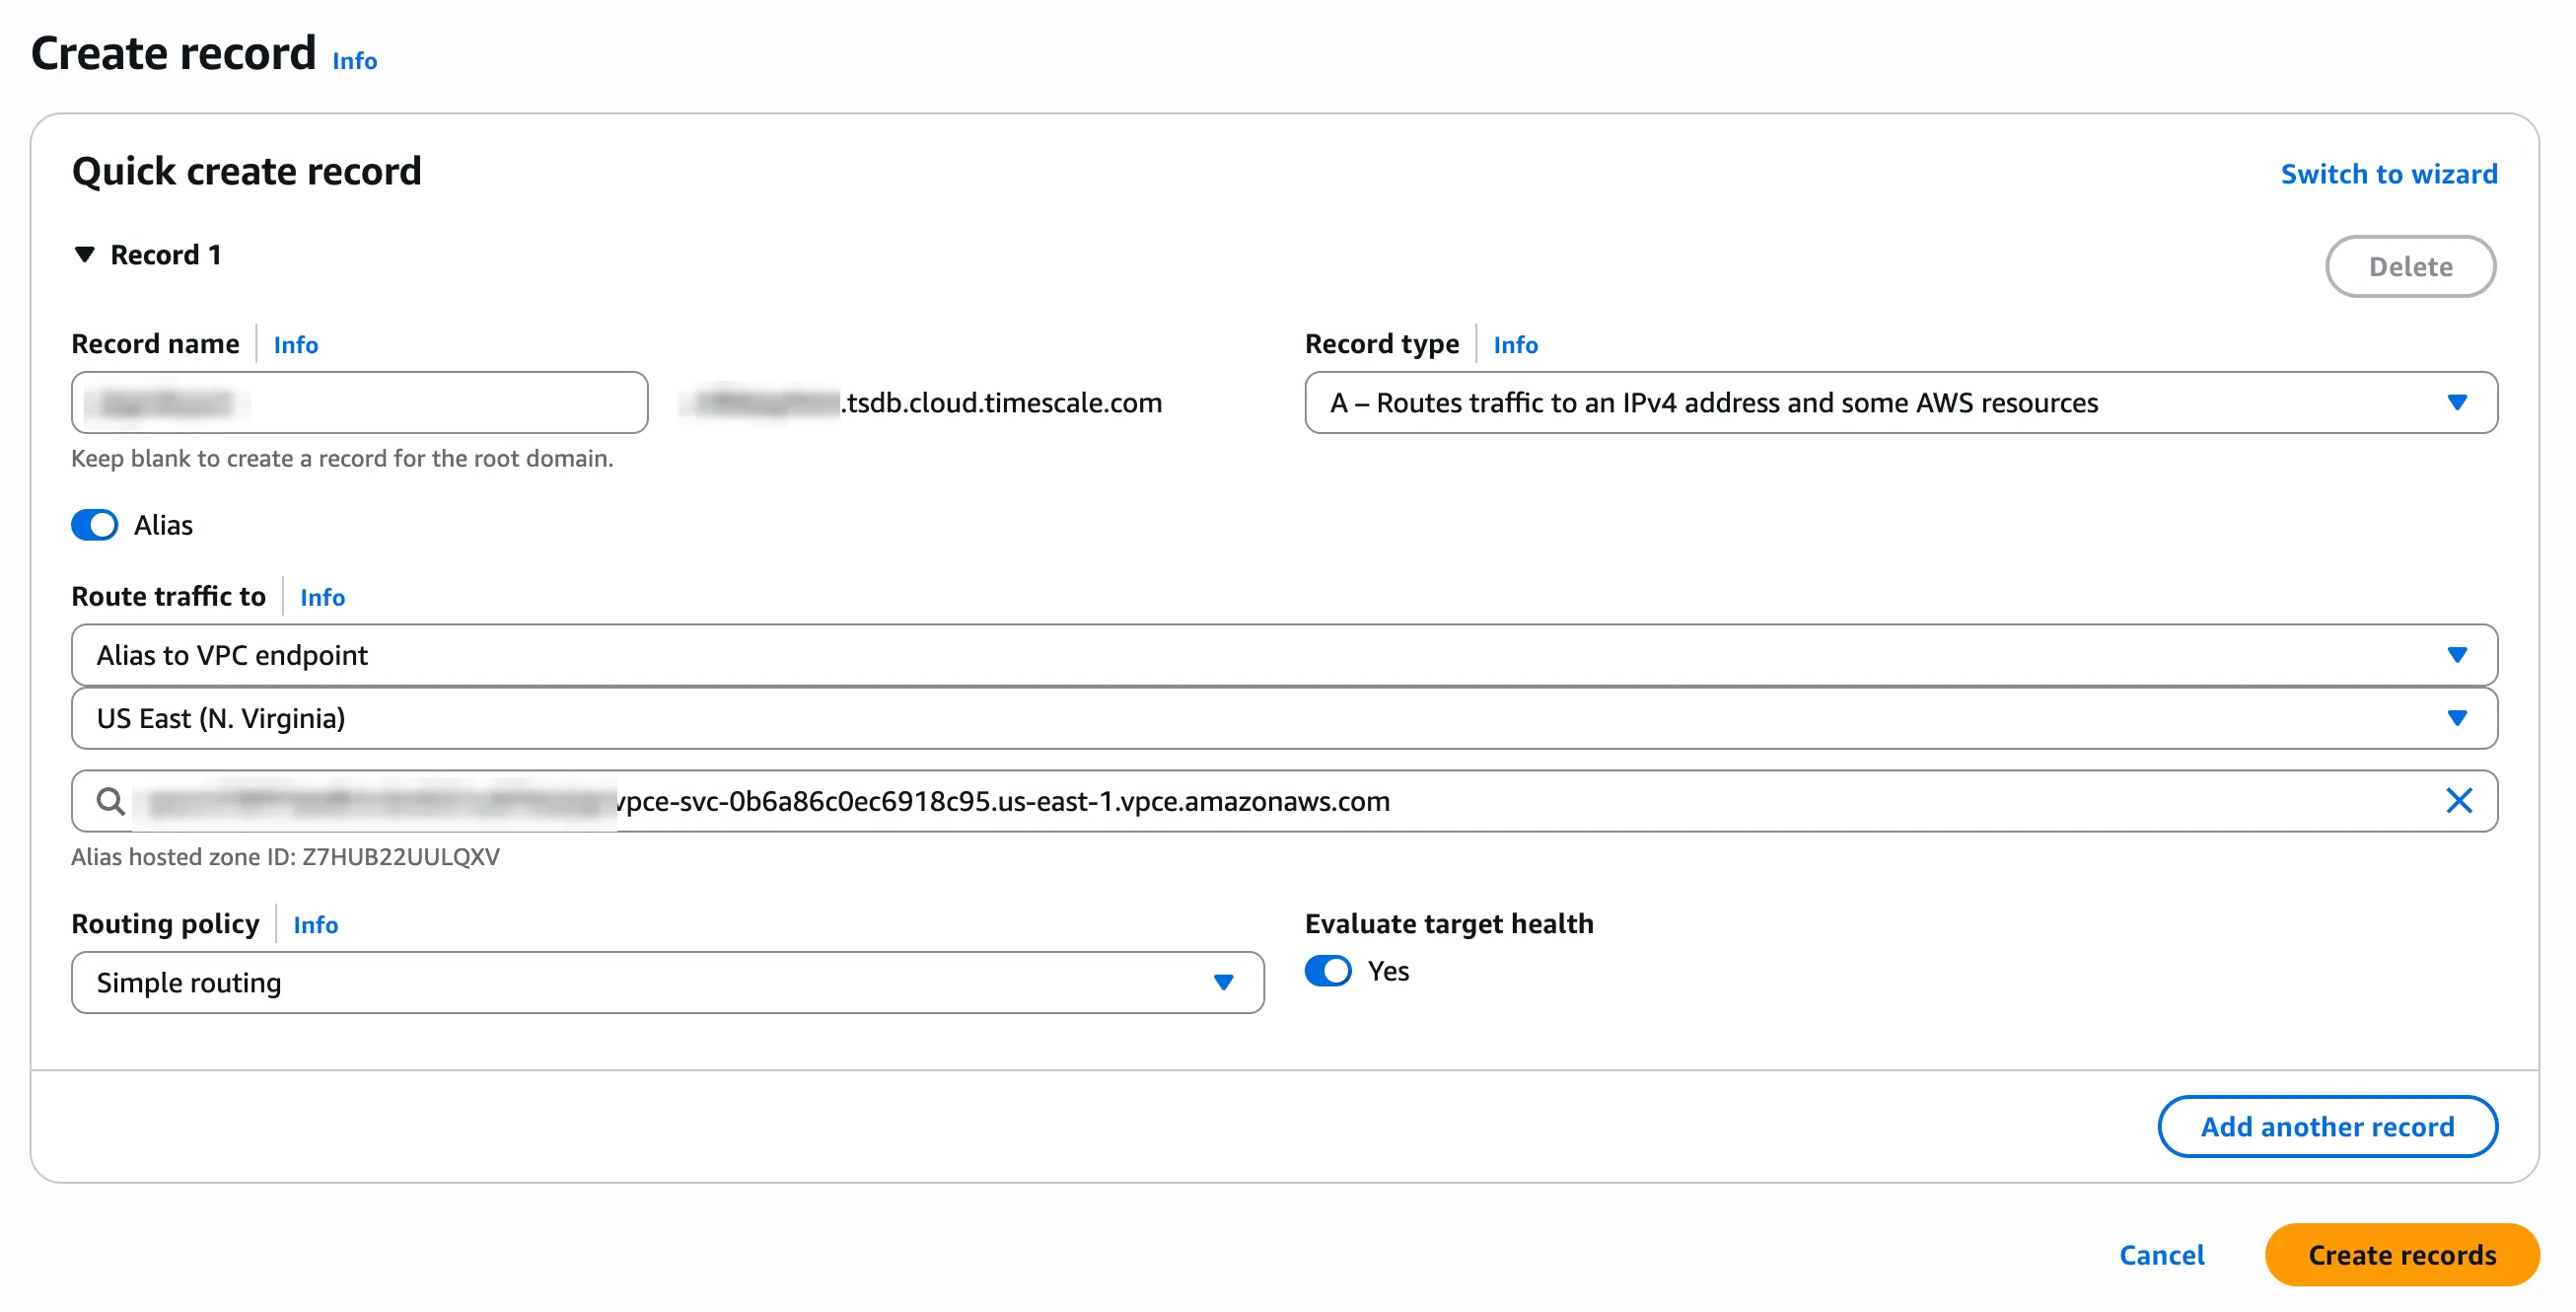
-
If your service has a read endpoint, add a second record for
<service-id>-repl.<project-id>.tsdb.cloud.timescale.com, pointing at the same VPC endpoint. This is the address of your service‘s replicas, shown asRead endpointin your connection details. -
If you use the connection pooler, it is reached at the primary hostname on its own port, so it needs no record of its own. Add the pooler port to your connection string instead.
Find your service ID and project ID in your connection details.
NoteYour private hosted zone overrides public DNS for everything under it, in every VPC you associate it with. A zone for
<project-id>.tsdb.cloud.timescale.comtakes over resolution for all services in that project, not only the ones you add records for. A hostname in that zone with no record returnsNXDOMAINinstead of falling back to the public address, so clients in those VPCs can no longer reach that service over the internet. Add a record for every service those clients connect to. -
- Test the connection
Run these from an EC2 instance inside the VPC you associated with the hosted zone. They fail from anywhere else, including your laptop, because the hostname resolves to private addresses.
-
Check that your zone resolves the hostname to your endpoint:
Terminal window dig +short <service-id>.<project-id>.tsdb.cloud.timescale.comYou get one private IP for each Availability Zone your endpoint spans. Two addresses means both zones can serve you. One address means the endpoint exists in a single Availability Zone and you have no failover.
No answer at all means the zone is not resolving. Check that the hosted zone is associated with this VPC, and that the record name matches the hostname exactly.
-
Check that the endpoint accepts connections on the port for this endpoint:
Terminal window nc -zv <service-id>.<project-id>.tsdb.cloud.timescale.com <port>A timeout here, rather than a refusal, usually means the endpoint’s security group does not allow inbound traffic on that port from this instance.
-
Connect, verifying the certificate:
Terminal window psql "postgres://tsdbadmin@<service-id>.<project-id>.tsdb.cloud.timescale.com:<port>/tsdb?sslmode=verify-full"sslmode=verify-fullis the point of publishing Tiger Cloud‘s hostname rather than the endpoint’s own name: it proves you reached your service privately and that the certificate matches. If this succeeds, your setup is correct. For how to supply the certificate and make this mode your default, see Connect with a stricter SSL mode. -
If you added a record for the read endpoint, repeat the check against it, using its own port:
Terminal window psql "postgres://tsdbadmin@<service-id>-repl.<project-id>.tsdb.cloud.timescale.com:<port>/tsdb?sslmode=verify-full"
WarningPorts are specific to each endpoint. Tiger Cloud uses the standard
5432where it can, but this is not guaranteed, and your primary and your read endpoint listen on different ports. Never assume a port: always use the one shown for that endpoint in your connection details. -
Migrate from a configured IP address
Section titled “Migrate from a configured IP address”If you set up PrivateLink before Tiger Cloud supported private DNS that you control, you configured your connection by adding the endpoint IP address in Tiger Console, and Tiger Cloud published the DNS records for you. That flow is retired.
To see whether this applies to you, open Security > Private Endpoints in Tiger Console and look at the IP Address column for your connection. If it is empty, you are already resolving through your own zone and you can skip this section. If it shows an address, follow the steps below to move to your own private DNS.
- Publish the hostname in your own zone
Create the records described in Publish the service hostname in your private DNS, then run the checks in Test the connection before you continue.
While your connection still has an IP address configured, the
digoutput shows which records are answering: one private IP per Availability Zone your endpoint spans means your own zone is live, and a single IP address means you are still resolving through the records Tiger Cloud publishes. If your endpoint spans a single Availability Zone, both answers are one address, so compare it against the IP address shown in Tiger Console instead. - Remove the IP address in Tiger Console
In
Security>Private Endpoints, remove the IP address from your connection. This deletes the DNS records that Tiger Cloud published and hands resolution to your zone.WarningYour own zone must already resolve the service hostname before you remove the IP address, otherwise connections fail until your DNS is in place. If that happens, add the IP address back in Tiger Console to restore the records Tiger Cloud publishes, then try again once your zone resolves the hostname.
Manage connections
Section titled “Manage connections”- To detach a service from a private endpoint connection, go to
Security>Private Endpoints, expand the arrow in theServicescolumn, and click the trash icon next to the service connection string. - To edit or remove an endpoint connection, go to
Security>Private Endpointsand click the three dots next to the connection in the list. SelectEditorDisconnect, respectively. You need to detach all services from a private endpoint connection before deleting it.